This article surveys 13 historically significant cyber attacks spanning from 2010 to 2021, ranging from state-sponsored infrastructure sabotage to massive data breaches affecting billions of users. The article documents how these incidents caused billions in damages, disrupted critical infrastructure and services, and fundamentally changed organizational approaches to cybersecurity. Understanding these attacks reveals the evolving sophistication of cyber threats and underscores why robust cybersecurity defenses are essential in the digital age.
- Stuxnet crossed physical-digital barrierStuxnet, discovered in 2010, was the first cyber weapon to cause actual physical destruction rather than just data theft or system disruption. It targeted Iranian nuclear facilities by infecting industrial control systems and secretly altering centrifuge speeds to cause equipment failure while making systems appear operational. The attack used multiple zero-day vulnerabilities, demonstrating that cyber operations could damage real-world infrastructure and fundamentally changing how governments view cyber warfare.
- WannaCry exploited known Windows flawThe 2017 WannaCry ransomware attack infected over 200,000 computers in more than 150 countries by exploiting the EternalBlue vulnerability in Microsoft Windows. The attack spread within hours across hospitals, banks, universities, transportation systems, and government agencies, with UK hospitals forced to cancel surgeries and turn away patients. The global cost exceeded $4 billion, making it one of the most damaging ransomware outbreaks ever recorded.
- Supply chain attacks reach thousandsThe SolarWinds attack represents a sophisticated supply-chain compromise where attackers inserted malicious code into legitimate software updates distributed by a network management company trusted by thousands of organizations. Over 18,000 organizations unknowingly installed the compromised update, giving attackers broad access to sensitive networks including government agencies, cybersecurity firms, technology companies, and defense contractors. This attack demonstrated how compromising a trusted intermediary can provide attackers with massive systemic access.
- Data breaches expose billions of accountsThe Yahoo data breach compromised approximately 3 billion user accounts between 2013 and 2014, making it the largest data breach ever recorded, and was not fully disclosed until years later. The Marriott breach exposed 500 million hotel customers' data including passport numbers and travel history, with attackers remaining undetected inside systems for years. The Equifax breach exposed 147 million people's sensitive data including Social Security numbers, birthdates, and driver's license information, creating serious identity theft risks.
- Ransomware targeted critical infrastructureThe 2021 Colonial Pipeline ransomware attack targeted the company responsible for transporting nearly half of the fuel used on the U.S. East Coast, forcing a complete pipeline shutdown to prevent further damage. This led to fuel shortages, panic buying, and rising fuel prices, with the company paying millions in ransom to regain system access. The attack demonstrated how ransomware against infrastructure providers creates cascading real-world consequences beyond financial loss.
- NotPetya destruction exceeded ransomware costNotPetya, which began in 2017, initially appeared to be ransomware but was actually designed to destroy data rather than collect payments, using stolen NSA hacking tools to spread rapidly through corporate networks. The attack affected major global companies including shipping giant Maersk and logistics companies worldwide, causing over $10 billion in global damages. The article identifies it as one of the costliest cyber attacks ever recorded, surpassing typical ransomware in its destructive intent and financial impact.
- Log4Shell vulnerability affected millions instantlyThe Log4Shell vulnerability discovered in 2021 existed in Log4j, a widely used Java logging library embedded in millions of applications and systems across the internet. Because Log4j was so pervasive in infrastructure, the vulnerability instantly put millions of servers at risk, prompting security teams worldwide to rush patching efforts. Security researchers described it as a 'catastrophic cybersecurity vulnerability' due to its widespread impact potential.
- IoT devices weaponized into botnetsThe Mirai botnet attack demonstrated how insecure internet-connected devices could be weaponized by malware that turned thousands of IoT devices—including security cameras, routers, and smart home devices—into a massive distributed denial-of-service (DDoS) attack network. The attack temporarily disrupted major portions of the internet by targeting websites including Twitter, Netflix, Reddit, and GitHub, revealing critical vulnerabilities in IoT device security practices.
Bottom line: The 13 cyber attacks documented show an escalating threat landscape where attackers exploit vulnerabilities across multiple attack vectors—from software flaws and supply chains to IoT devices and industrial systems—causing billions in damages and exposing billions of user accounts. Organizations must implement continuous software patching, advanced threat detection, security audits, and employee training while monitoring official alerts from agencies like CISA to defend against increasingly soph
Today, cyber warfare has become a serious global threat. Governments and companies are investing heavily in cyber defense, while cybercriminals continue to develop more advanced hacking techniques. Understanding the most dangerous cyber attacks in history helps reveal how hackers operate, what vulnerabilities they exploit, and why cybersecurity has become one of the most critical challenges of the digital age.
In this article, we will explore 13 of the most dangerous cyber attacks ever happened, including ransomware outbreaks, massive data breaches, state-sponsored cyber warfare, and sophisticated hacking campaigns that shocked the world.
Some of these attacks caused billions of dollars in losses, while others exposed sensitive information belonging to millions of users. Each of these incidents left a lasting impact on global cybersecurity and forced organizations to rethink how they protect their systems. By studying these major cyber attacks, we can better understand how cyber threats evolve — and why strong cybersecurity practices are more important today than ever before.
Let’s dive into the 13 cyber attacks that changed the internet forever.
Table of Contents
13 Most Dangerous Cyber Attacks in History (Explained)
Cyber attacks have evolved from simple hacking attempts to highly sophisticated digital warfare operations. The most dangerous cyber attacks in history have disrupted governments, corporations, and global infrastructure, causing billions of dollars in damage.
Many cyber attacks begin with malicious software. Learn more in our guide on What Is Malware and How It Works.
Below are 13 of the most dangerous cyber attacks ever recorded, each of which had a massive impact on cybersecurity.
1. Stuxnet – The First Cyber Weapon
The Stuxnet attack is widely considered one of the most dangerous cyber attacks in history because it was the first known cyber weapon designed to cause physical destruction.
Discovered in 2010, Stuxnet targeted Iran’s nuclear program by infecting industrial control systems used in nuclear centrifuges. The malware secretly altered the speed of centrifuges, causing them to break while appearing to operate normally.
What made Stuxnet particularly dangerous was its complexity. The malware used multiple zero-day vulnerabilities, making it extremely difficult to detect.
Key facts about the Stuxnet cyber attack:
- discovered in 2010
- targeted Iranian nuclear facilities
- used multiple zero-day vulnerabilities
- sabotaged industrial equipment
Impact:
The attack demonstrated that cyber weapons could damage real-world infrastructure, changing how governments approach cyber warfare and national security.
2. WannaCry Ransomware Attack
The WannaCry ransomware attack in 2017 quickly became one of the most dangerous cyber attacks in history.
This ransomware spread rapidly across the world by exploiting a vulnerability in Microsoft Windows known as EternalBlue.
Within hours, the malware infected more than 200,000 computers in over 150 countries.
Victims included:
- hospitals
- banks
- universities
- transportation systems
- government agencies
Hospitals in the United Kingdom were particularly affected, forcing medical staff to cancel surgeries and turn away patients.
Impact:
The global cost of the WannaCry cyber attack is estimated to be over $4 billion, making it one of the most damaging ransomware outbreaks ever.
You can read in detail about what is ransomware and how it works in our detailed article.
3. NotPetya – The $10 Billion Cyber Attack
The NotPetya cyber attack initially appeared to be ransomware but was actually designed to destroy data rather than collect payments.
The attack began in 2017 and spread rapidly through corporate networks using advanced propagation techniques.
Major global companies were affected, including shipping giant Maersk and logistics companies worldwide.
Key characteristics of the NotPetya attack:
- used stolen NSA hacking tools
- spread rapidly across networks
- destroyed critical data
Impact:
The NotPetya attack caused over $10 billion in global damages, making it one of the costliest cyber attacks ever recorded.
4. SolarWinds Supply Chain Attack
The SolarWinds cyber attack is considered one of the most sophisticated cyber espionage campaigns in history.
Hackers compromised the software update system of SolarWinds, a company that provides network management software used by thousands of organizations.
The attackers inserted malicious code into legitimate software updates, which were then downloaded by victims.
Affected organizations included:
- government agencies
- cybersecurity firms
- technology companies
- defense contractors
Impact:
More than 18,000 organizations installed the compromised software update, giving attackers access to sensitive networks worldwide.
5. Equifax Data Breach
The Equifax data breach exposed sensitive personal data belonging to 147 million people.
Hackers exploited a vulnerability in the company’s web application software.
The stolen data included:
- Social Security numbers
- birth dates
- home addresses
- driver’s license numbers
Because Equifax is a credit reporting agency, the stolen data created serious risks of identity theft.
Impact:
The company faced massive lawsuits and regulatory fines, and the breach became one of the largest identity data exposures in history.
6. Yahoo Data Breach
The Yahoo data breach remains the largest data breach ever recorded.
Hackers compromised Yahoo’s systems between 2013 and 2014, affecting approximately 3 billion user accounts.
The attackers gained access to:
- email addresses
- passwords
- security questions
- account recovery data
The breach was not fully disclosed until several years later, which sparked major criticism of Yahoo’s security practices.
Impact:
This cyber attack significantly reduced Yahoo’s company value during its acquisition by Verizon.
7. Colonial Pipeline Ransomware Attack
The Colonial Pipeline cyber attack in 2021 highlighted the real-world consequences of ransomware.
Hackers targeted the pipeline company responsible for transporting nearly half of the fuel used on the U.S. East Coast.
After the ransomware attack was discovered, the company shut down pipeline operations to prevent further damage.
Consequences included:
- fuel shortages
- panic buying
- rising fuel prices
Impact:
The company paid millions of dollars in ransom to regain access to its systems.
8. Target Data Breach
The Target cyber attack in 2013 compromised payment information belonging to 40 million customers.
Hackers gained access to Target’s network through a third-party vendor that had access to the company’s systems.
Once inside, attackers installed malware on the company’s point-of-sale systems to capture credit card data.
Impact:
The breach resulted in:
- massive financial losses
- lawsuits and settlements
- major changes to retail cybersecurity practices
9. Sony Pictures Hack
The Sony Pictures cyber attack exposed confidential corporate information and internal communications.
Hackers leaked:
- unreleased movies
- private employee records
- confidential emails
- business strategies
The breach caused serious reputational damage and disrupted Sony’s operations.
Impact:
The attack demonstrated how cyber attacks can be used for political or ideological purposes, not just financial gain.
10. Operation Aurora
Operation Aurora was a highly sophisticated cyber espionage campaign discovered in 2010.
The attack targeted multiple major technology companies, including Google.
Hackers exploited a zero-day vulnerability in Internet Explorer to gain access to company networks.
The attackers attempted to access intellectual property and monitor communications.
Impact:
The attack forced Google to reevaluate its cybersecurity strategy and strengthened industry awareness of advanced persistent threats.
11. Mirai Botnet Attack
The Mirai botnet attack demonstrated how insecure IoT devices could be used to launch massive cyber attacks.
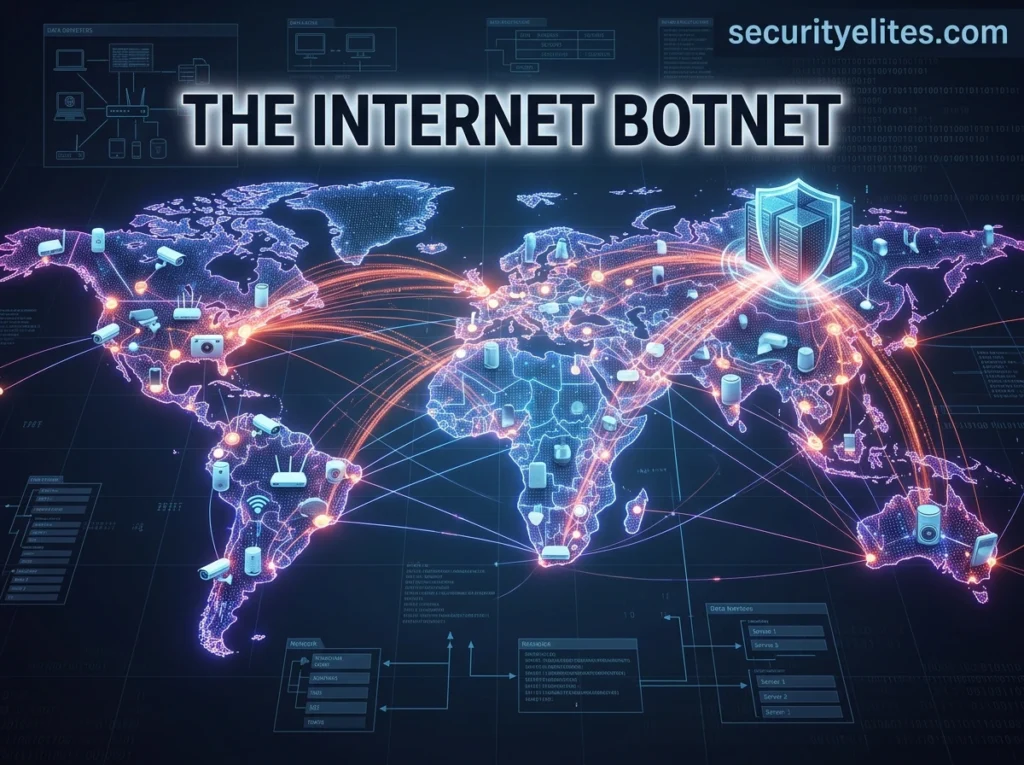
The malware infected thousands of internet-connected devices such as:
- security cameras
- routers
- smart home devices
These devices were then used to launch a massive distributed denial-of-service (DDoS) attack.
Major websites affected included:
- Netflix
- GitHub
Impact:
The attack temporarily disrupted major parts of the internet.
12. Marriott Data Breach
The Marriott cyber attack exposed the personal data of 500 million hotel customers.
Hackers gained access to the company’s reservation database and remained inside the system for years before being detected.
The stolen data included:
- passport numbers
- travel history
- personal contact details
Impact:
The breach triggered major investigations and raised concerns about long-term data security.
13. Log4Shell Vulnerability Crisis
The Log4Shell vulnerability discovered in 2021 became one of the most dangerous software vulnerabilities ever found.
The vulnerability existed in Log4j, a widely used Java logging library used by millions of applications.
Because Log4j was embedded in countless systems, millions of servers were instantly at risk.
Security teams worldwide rushed to patch systems to prevent exploitation. Security researchers track newly discovered vulnerabilities through the CVE vulnerability database maintained by MITRE, which catalogs thousands of known cybersecurity flaws used in cyber attacks.
Impact:
Experts described Log4Shell as a “catastrophic cybersecurity vulnerability” due to its widespread impact.
FAQs: Most Dangerous Cyber Attacks in History
What are the most dangerous cyber attacks in history?
The most dangerous cyber attacks in history include Stuxnet, WannaCry, NotPetya, SolarWinds, and the Yahoo data breach. These attacks caused billions of dollars in damage, disrupted global infrastructure, and exposed the personal data of millions of users worldwide.
Which cyber attack caused the most financial damage?
The NotPetya cyber attack is considered one of the costliest cyber attacks ever recorded. It caused more than $10 billion in global damages, affecting major international companies and disrupting logistics, shipping, and manufacturing operations.
What was the largest data breach in history?
The Yahoo data breach is the largest data breach ever discovered. Hackers compromised approximately 3 billion user accounts, exposing email addresses, passwords, and account security information.
What was the first cyber weapon used in warfare?
The Stuxnet malware attack is widely considered the first cyber weapon used in modern warfare. The malware targeted Iranian nuclear facilities and sabotaged industrial centrifuges using sophisticated code and multiple zero-day vulnerabilities.
Why are cyber attacks becoming more common?
Cyber attacks are increasing because organizations rely heavily on digital systems, while hackers continue developing advanced attack methods such as ransomware, phishing, botnets, and zero-day exploits.
What industries are most targeted by cyber attacks?
Cybercriminals frequently target industries that store valuable data, including:
- healthcare
- financial services
- government agencies
- technology companies
- retail organizations
These sectors contain sensitive information that can be exploited or sold on the dark web.
How can companies protect themselves from cyber attacks?
Organizations can reduce cyber risks by implementing strong cybersecurity practices such as:
- keeping software updated
- using advanced threat detection tools
- conducting regular security audits
- training employees to recognize phishing attacks
These measures help prevent major cyber incidents. Organizations can monitor emerging cyber threats through official alerts published by the Cybersecurity and Infrastructure Security Agency (CISA).
What is the difference between a cyber attack and a data breach?
A cyber attack is an attempt by hackers to gain unauthorized access to systems or networks. A data breach occurs when attackers successfully steal or expose sensitive information such as personal data, passwords, or financial records.
Conclusion
The most dangerous cyber attacks in history demonstrate how powerful cyber threats have become.
From ransomware outbreaks to nation-state cyber warfare, these incidents highlight the importance of strong cybersecurity practices.
As technology continues to evolve, organizations and individuals must remain vigilant against emerging threats and continuously strengthen their digital defenses.
Understanding these attacks helps security professionals learn from past incidents and build stronger protections for the future.
