AI LLM Hacking Course
+5 XP
Category
Ethical Hacking
Learn ethical hacking step-by-step with practical tutorials, real-world attack simulations, and penetration testing labs. This category covers reconnaissance, footprinting, network scanning, enumeration, exploitation, privilege escalation, sniffing, session hijacking, and social engineering techniques used by professional ethical hackers. You’ll also explore industry-standard tools like Metasploit, Burp Suite, and Nmap while practicing in safe lab environments. Whether you’re a beginner or advanced learner, these ethical hacking guides will help you understand how hackers think and how to defend systems against cyber threats.
385 articles
MCP Security
+5 XP
Prompt Injection through MCP — The Complete 2026 Beginner’s Guide | MCP Security Day 3 of 7
Prompt injection through MCP attacks explained — how resource-channel injection hijacks AI assistants, the payload patterns to recognise, and real…
Ethical Hacking Course
+5 XP
How to perform credential Harvesting – DUMP LSASS, SAM, NTDS and Browser Passwords | Ethical Hacking Course Day 42 of 100
Credential harvesting — learn where Windows stores credentials, how attackers extract them with Impacket secretsdump, and how blue teams detect…
Bug Bounty Course
+5 XP
Deserialization Bug Bounty — Find, Exploit, Report Java, PHP and Python Unsafe Deserialization | Bug Bounty Course Day 30 of 60
Deserialization bug bounty — learn to find and report unsafe deserialization in Java, PHP and Python apps with Burp Suite…
MCP Security
+5 XP
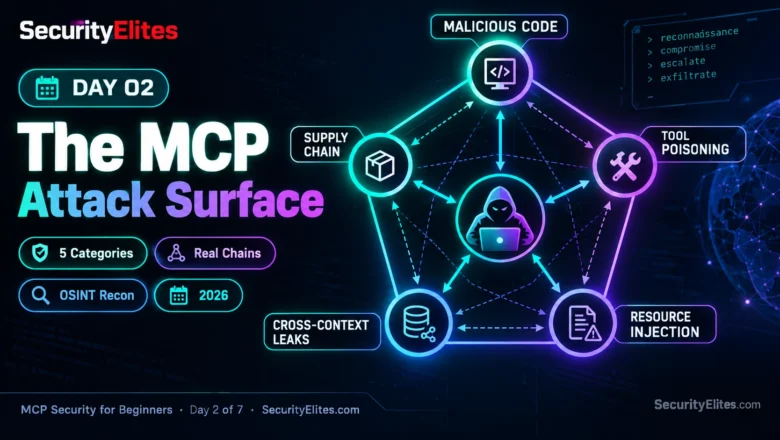
MCP Attack Surface — The 2026 Beginner’s Complete Map | MCP Security — Day 2 of 7
MCP attack surface explained — the five categories every developer must know in 2026, with real attack chains and defensive…
AI LLM Hacking Course
+5 XP
How to Assess AI Social Engineering Risk in 2026 | AI LLM Hacking Course Day 42 of 90
Master AI social engineering assessment in 2026. How AI amplifies spear phishing, vishing, deepfake impersonation, AI assistant manipulation and defending…
AI Deepfake
+5 XP
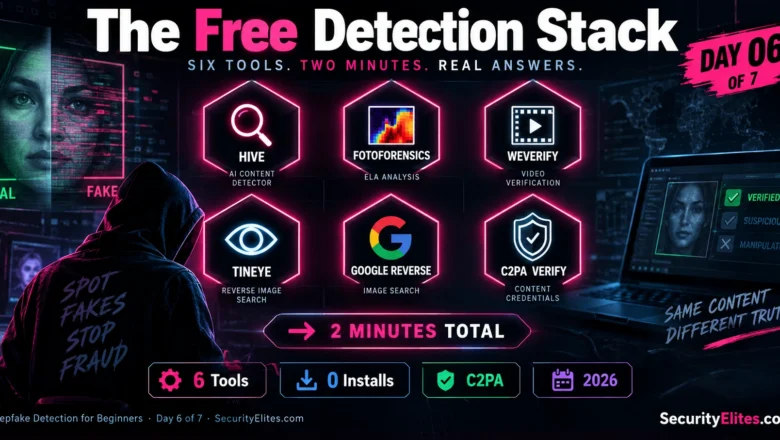
Deepfake Detection Tools Free — Complete 2026 Kit and 6-Tool Workflow | Deepfake Detection for Beginners — Day 6 of 7
Deepfake detection tools free — the complete 2026 six-tool browser stack, decision tree, and C2PA content credentials workflow for detection.
Ethical Hacking Course
+5 XP
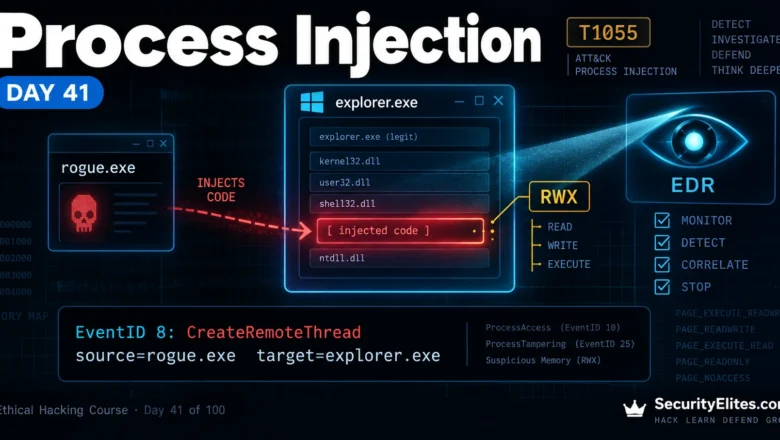
Process Injection — How Malware Hides in Trusted Processes & How to Catch It | Ethical Hacking Course Day 41 of 100
Process injection detection — understand how malware hides inside trusted processes and learn the Sysmon, memory and behavioural signals that…
Kali Linux Course
+5 XP
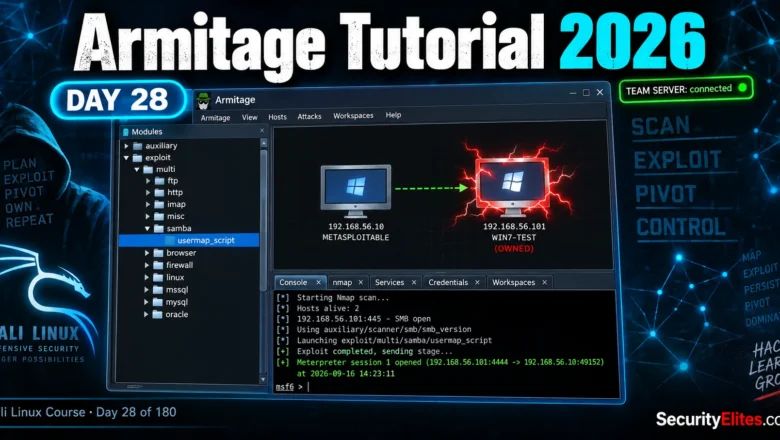
Armitage Tutorial 2026 — Metasploit GUI, Team Server Guide | Kali Linux Course Day 28
Master Armitage tutorial 2026 — drive Metasploit from a GUI, run a team server, scan and exploit a Metasploitable lab,…
AI Deepfake
+5 XP
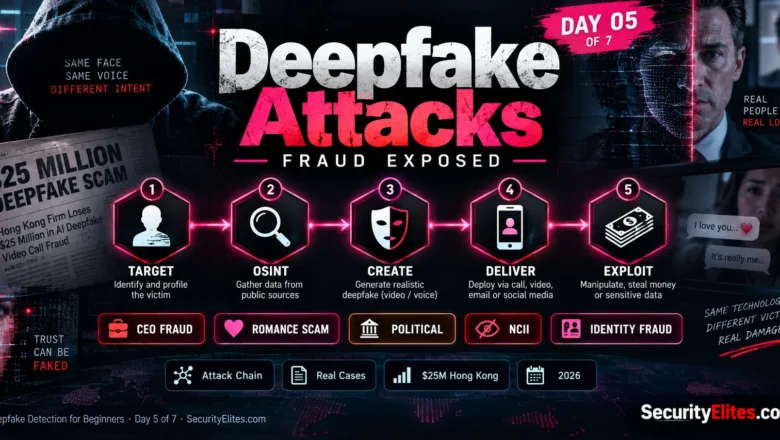
Deepfake Attacks Fraud Exposed — Real 2025-2026 Cases | Deepfake Detection for Beginners — Day 5 of 7
Deepfake attacks fraud explained — real 2025-2026 cases, the full attack chain criminals use, and how to recognise when you're…