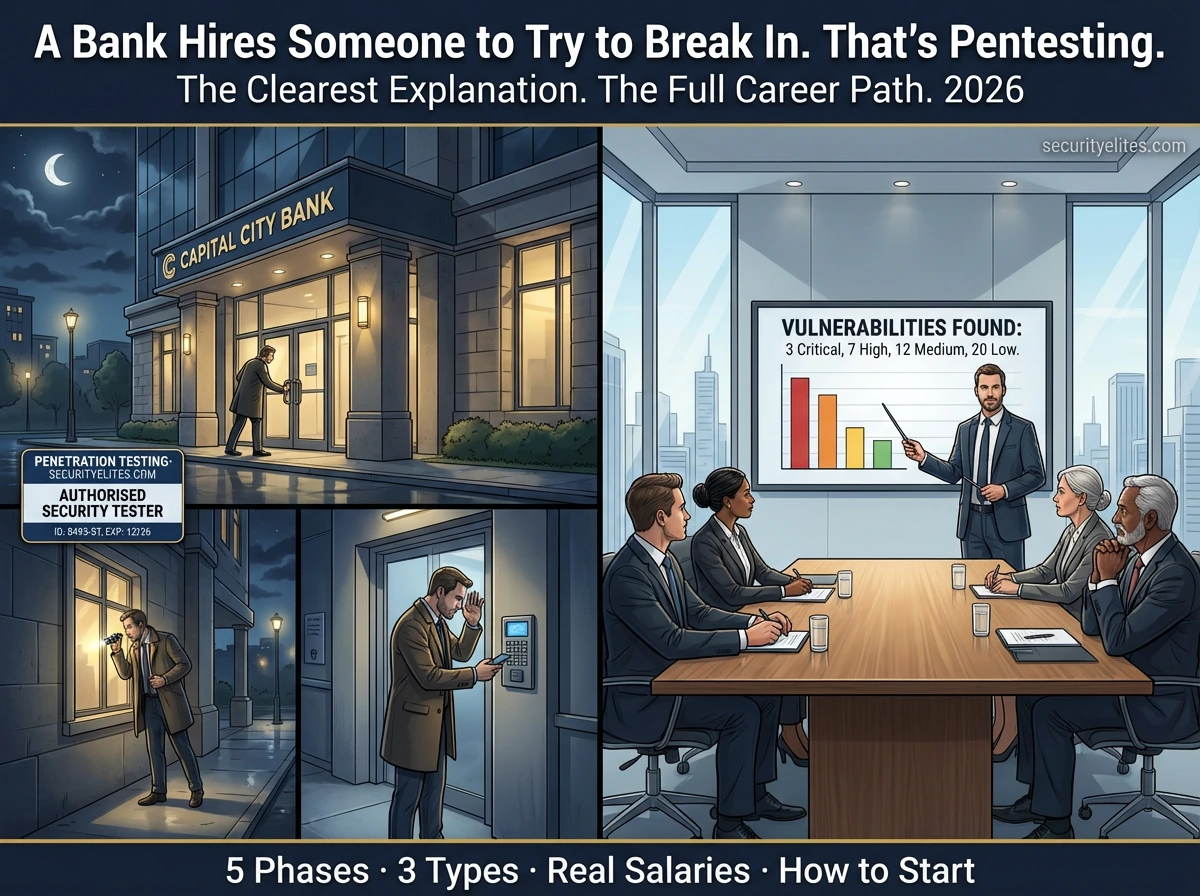
This article explains penetration testing as a structured, authorized security assessment where professionals simulate cyberattacks to find vulnerabilities before criminals do. It covers the definition, five-phase methodology, testing types, practical workflow, career information, and key distinctions from related disciplines. The article demonstrates that penetration testing is a methodical, documentation-heavy profession focused on identifying and communicating security weaknesses rather than dramatic hacking activities.
- Three requirements for legitimate penetration testingEvery authorized pentest must have explicit written authorization (a signed contract), a defined scope specifying what systems and methods are in and out of bounds, and a professional report documenting vulnerabilities with severity ratings and remediation steps. Without written authorization, the same activities constitute criminal hacking regardless of intent. The report is the primary deliverable clients pay for.
- Five-phase methodology every engagement followsPhase 1 (Reconnaissance) gathers intelligence passively using WHOIS, LinkedIn, and Shodan without triggering alerts. Phase 2 (Scanning and Enumeration) actively probes for vulnerabilities using tools like Nmap and Nikto. Phase 3 (Exploitation) demonstrates real impact using Metasploit and custom scripts. Phase 4 (Post-Exploitation) assesses damage through privilege escalation and lateral movement using tools like Bloodhound and Meterpreter. Phase 5 (Reporting) converts findings into actionable executive and technical documentation.
- Black, grey, and white box testing modelsBlack box simulates an external attacker with zero prior knowledge, most realistic but most challenging. Grey box (the most common type) assumes a compromised account with partial credentials and documentation, balancing realism with testing efficiency. White box provides full source code and architecture access, enabling deepest vulnerability detection but not simulating realistic external threats, suited for code security audits.
- Penetration testing versus related engagement typesPenetration testing uses a signed contract with defined scope and fixed fee, delivering a full professional report. Bug bounty programs operate under open-ended program policy with per-finding payments and individual finding reports. Ethical hacking is the broader concept covering any authorized security testing, making penetration testing a specific structured subset of ethical hacking rather than synonymous terms.
- Daily work is reconnaissance and documentation heavyA typical penetration tester's day involves kickoff calls, reconnaissance through subdomain enumeration and DNS queries, comprehensive scanning with Nmap and Burp Suite, exploitation confirmation (like identifying SQL injection with screenshots), and report writing beginning the same day. The actual exploitation phase represents a relatively small portion of total engagement time, with most work spent on information gathering, analysis, and documentation.
- Career progression and 2026 salary rangesJunior pentesters (0-2 years) with eJPT level earn $55K-$75K annually. Mid-level professionals (2-5 years) with OSCP certification earn $80K-$110K. Senior testers (5+ years) and specialists earn $120K-$180K yearly. Independent consultants bill $150-$250 per hour. The article indicates penetration testing is among the highest-paying entry-level technology roles available.
- Career entry path follows 12-month progressionFoundational skills (networking, Linux, web fundamentals) take three months. Months 3-6 involve hands-on practice in legal environments using home labs and platforms like TryHackMe and Hack The Box. Certification (eJPT) occurs around months 6-9. The final phase involves building a portfolio through CTF write-ups on GitHub, bug bounty findings, and applying for junior roles by month 12.
Bottom line: Penetration testing is a structured, authorized security profession where professionals systematically find vulnerabilities using real-world attack techniques and deliver professional reports enabling organizations to fix weaknesses before attackers exploit them. Success in this field requires technical skills across five methodical phases, strong documentation and communication abilities, and adherence to strict legal and authorization requirements that distinguish legitimate security testing f
What Is Penetration Testing — The Complete Definition
Penetration testing (also called a pentest, pen test, or ethical hacking engagement) is a structured, authorised security assessment in which a security professional simulates a real cyberattack against an organisation’s systems, applications, or network to identify exploitable vulnerabilities before malicious actors can find and exploit them.
Penetration Testing vs Ethical Hacking vs Bug Bounty
These three terms are often used interchangeably but describe different engagement models. Understanding the distinction matters for your career path:
| Model | Authorisation | Structure | Payment | Deliverable |
|---|---|---|---|---|
| Penetration Testing | Signed contract | Defined scope + timeline | Fixed fee (upfront) | Full professional report |
| Bug Bounty | Programme policy | Open-ended, programme scope | Per valid finding | Individual finding reports |
| Ethical Hacking (broad) | Any written permission | Variable | Variable | Variable |
The 5 Phases Every Professional Penetration Test Follows
3 Types of Penetration Testing: Black Box, Grey Box, White Box
A Day in the Life of a Penetration Tester
Penetration Tester Salaries 2026
How to Start a Penetration Testing Career From Zero
The penetration testing career path is well-documented at SecurityElites.com — our free courses and guides cover every step from no experience to employed professional:
Frequently Asked Questions
→ Free Ethical Hacking Course — eJPT Preparation
Bug Bounty Hunting for Beginners — Step-by-Step Guide
Kali Linux Commands Cheat Sheet 2026 — 200+ Commands
Offensive Security PEN-200 (OSCP) Official Page →
TCM Security PNPT Official Page →
INE Security eJPT Official Page →
The bank analogy in the opening is the one I use when non-technical people ask what I do for a living. It works every time because it communicates the core truth: this profession exists because organisations need to know their weaknesses before adversaries exploit them. The job is finding those weaknesses first, in a controlled way, and communicating them clearly enough that they get fixed.
