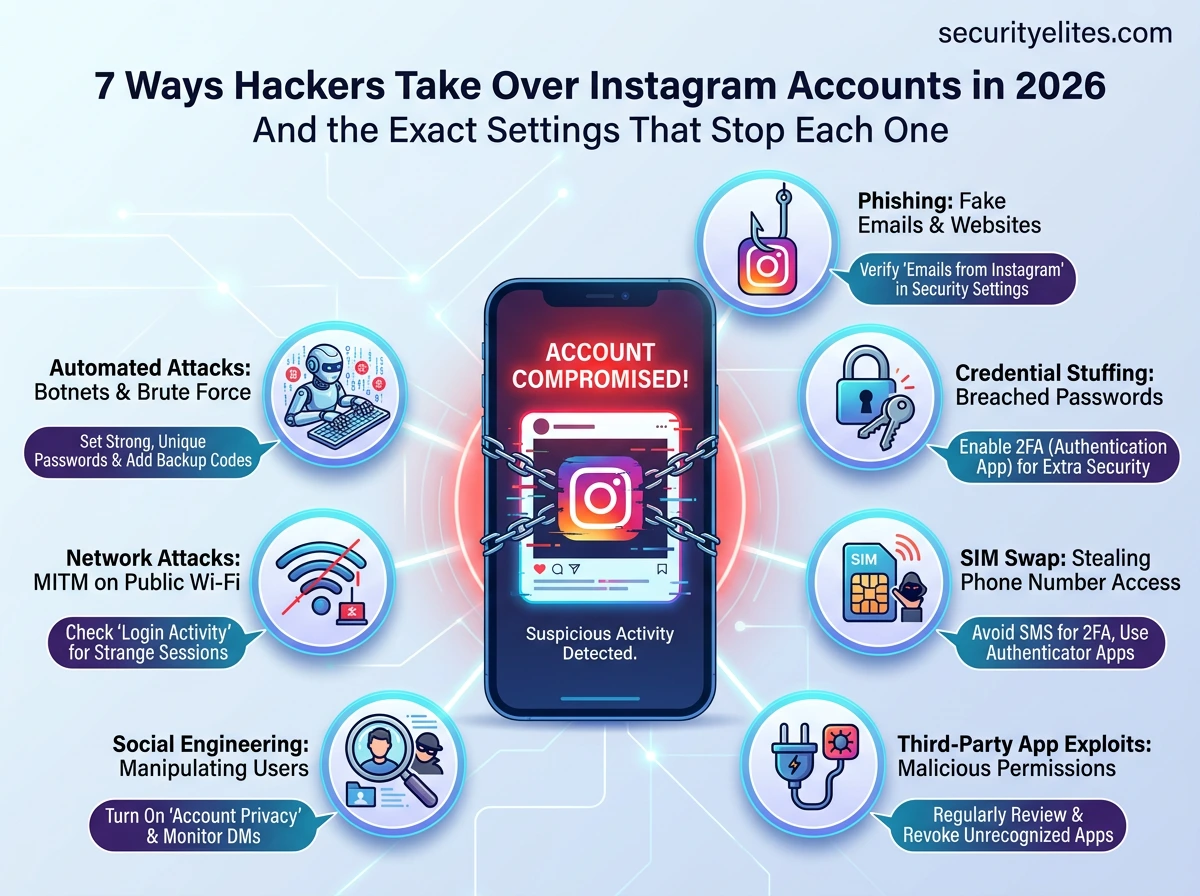
This article identifies and explains seven well-documented methods by which Instagram accounts are compromised, emphasizing that most attacks exploit simple security gaps rather than technical sophistication. The article addresses the problem that 76% of Instagram users have never configured basic security settings, leaving accounts vulnerable to automated attack tools. Understanding these attack vectors and their specific defenses is critical because compromises are preventable through straightforward protective actions.
- Phishing remains the dominant attack vectorPhishing consistently ranks as the leading cause of Instagram account compromise and works by creating fake login pages that mimic Instagram's interface. Attacks arrive via DMs, emails, SMS, and QR codes, using manufactured urgency (fake 24-hour account deletion threats) to panic users into clicking malicious links that direct to domains like instagram-support-verify.com rather than instagram.com. The article demonstrates that even security-aware users get caught because phishing pages are now sophisticated enough to deceive them.
- Credential stuffing exploits password reuse across sitesOver 15 billion username-password combinations from thousands of past data breaches (LinkedIn 2012, Adobe 2013, Yahoo 2016, Dropbox 2012) are actively circulating on criminal forums and tested against Instagram through automated tools. If an Instagram user's password matches any password they previously used on any breached site, attackers may already have attempted access or will do so. The defense requires using a unique, randomly generated password for Instagram that exists nowhere else, making reused credentials ineffective.
- SIM swapping targets phone number verificationAttackers collect publicly available personal information from social media profiles (full name, birthday, address, phone hints), then impersonate users to their mobile carriers and request SIM transfers to attacker-controlled cards. Once successful, the attacker receives all SMS messages intended for the user, including two-factor authentication codes and password reset links, compromising the account within minutes. This attack specifically targets high-value accounts like influencers and business accounts.
- Third-party apps grant persistent unauthorized accessWhen users click 'Continue with Instagram' or 'Connect your Instagram account' on follower trackers, schedulers, growth tools, or contest apps, they grant OAuth tokens with ongoing access that persists indefinitely—even if the password changes or the app is later sold to malicious operators. Many of these apps are built specifically to harvest account data or maintain persistent access, and removal requires manually revoking them through Settings → Security → Apps and Websites.
- Social engineering manipulates people and support staffAttackers impersonate public figures to convince Instagram support to transfer accounts, send fake collaboration offers with credential-harvesting links, pose as mutual contacts to distribute phishing links, or pose as Instagram's verification team offering blue checkmarks for login credentials. Red flag DMs include requests for login credentials, paid collaboration links with urgent deadlines, and unverified prize claims, whereas legitimate opportunities come from company domain emails and verified official channels.
- Weak passwords exploit personal information visibilityAttackers build personalized wordlists from publicly visible Instagram profile data—usernames, pet names from posts, birth years, partner names from tagged photos, and favorite football teams from bios—making passwords like 'Rajesh1990' or 'Chelsea2026' guessable in seconds. The article emphasizes that password strength must derive from completely random characters (e.g., xK#9mP$2wL@nR7qT) or random passphrases with no personal information, generated through password managers like Bitwarden.
- Malware steals session cookies without passwordsInformation stealer malware variants (Redline, Raccoon, Vidar) copy browser session cookies that keep users logged into Instagram, allowing attackers to authenticate as the user without knowing passwords, bypassing two-factor authentication, or triggering Instagram's login detection systems. These stealers arrive via cracked software downloads, malicious email attachments, unofficial browser extensions, Discord servers, fake VPN applications, and fake Instagram desktop apps. Defense requires downloading only from official sources, maintaining updated antivirus software, reviewing browser exten
- Two-factor authentication must use apps, not SMSWhile two-factor authentication is essential against phishing and credential stuffing, SMS-based 2FA is vulnerable to SIM swapping, which intercepts the text message codes. The article specifies that authenticator apps (which generate codes locally on the device) cannot be intercepted by SIM swap attackers, making them the required defense against that attack vector. Additionally, adding a PIN or port freeze to carrier accounts prevents SIM transfers without the PIN.
Bottom line: All seven Instagram compromise methods are preventable through straightforward actions: using unique passwords with a password manager, enabling authenticator-app-based two-factor authentication, verifying links before clicking them, auditing connected third-party apps, and downloading software only from official sources. The article's core argument is that Instagram account security depends almost entirely on user awareness and basic configuration, not technical sophistication, because the atta
METHOD 1
Phishing — How Instagram Accounts Get Hacked Most Often
Phishing is consistently the leading cause of Instagram account compromise. The concept is simple: create a website that looks exactly like Instagram’s login page, trick you into visiting it, and collect your credentials when you enter them. In 2026, phishing pages are sophisticated enough that even security-aware users get caught off-guard.
The delivery mechanisms evolve constantly: Instagram DMs claiming your account was reported for copyright infringement, emails with urgent warnings about account deletion, SMS messages from fake Instagram numbers, and even QR codes at physical locations. The urgency is always manufactured, the timeline is always fake (“your account will be disabled in 24 hours”), and the link always leads somewhere that is not instagram.com.
Your account will be permanently disabled within 24 hours unless you verify your identity at the link below.
METHOD 2
Credential Stuffing — Your Other Passwords Are the Problem
Here is something most people do not realise: over 15 billion username and password combinations are circulating on criminal forums right now, collected from thousands of data breaches over the past decade. LinkedIn’s 2012 breach. Adobe’s 2013 breach. Yahoo’s 2016 breach. These breaches exposed hundreds of millions of real credentials — and they are still being used today.
Credential stuffing is the automated process of taking these breached credentials and trying them against Instagram. If your email address is you@gmail.com and your Instagram password is the same as any password you have ever used on any other site that was breached, attackers may already have tried it — or will soon.
Check if your email or phone has appeared in a data breach
METHOD 3
SIM Swapping — How Instagram Accounts Get Hacked Through Your Phone Number
SIM swapping targets high-value accounts — influencers, business accounts, public figures. The attacker collects personal information about you from public social media profiles (your name, date of birth, address — information you likely share openly), then calls your mobile carrier pretending to be you reporting a lost phone. They request your number be transferred to their new SIM card. If they succeed, your phone loses signal and they now receive all calls and SMS messages intended for you — including two-factor authentication codes and password reset links.
METHOD 4
Malicious Third-Party Apps — The Access You Gave Away
Every time you click “Continue with Instagram” or “Connect your Instagram account” to a third-party app — a follower tracker, a scheduler, a growth tool, a contest entry — you grant that app an OAuth token with ongoing access to your Instagram account. This access persists indefinitely unless you revoke it, regardless of whether you change your Instagram password.
Many of these apps are legitimate and useful. But many are built specifically to harvest account data or maintain persistent access. A “free follower boost” app that you connected in 2021 may still have active access to your Instagram account today — even if the app has been sold to a malicious operator since then.
METHOD 5
Social Engineering — Targeting Support and Your Contacts
Social engineering attacks target people rather than systems. Against Instagram specifically, this includes: impersonating a public figure to convince Instagram support to transfer an account, sending fake “collaboration offers” to influencers that include credential-harvesting links, pretending to be a mutual contact to trick someone into clicking a phishing link, or posing as Instagram’s verification team offering a “blue tick” in exchange for login credentials.
METHOD 6
Weak and Guessable Passwords — Attackers Know You Better Than You Think
Weak password attacks go beyond simple brute force. Attackers build personalised wordlists from publicly available information — your name, your pet’s name from Instagram posts, your birth year, your partner’s name from tagged photos, your favourite football team from your bio. A password like Rajesh1990 or Chelsea2026 takes seconds to guess when the attacker can see your profile.
xK#9mP$2wL@nR7qT or passphrase-style: purple-lamp-kite-83-summit. Neither is guessable from your Instagram profile. Bitwarden is free and generates these automatically.
METHOD 7
Malware and Session Cookie Theft — The Invisible Attack
Malware specifically designed to steal browser session cookies — called “information stealer” malware — is a growing threat. When you log into Instagram, your browser stores a session cookie that keeps you logged in. Information stealers (Redline, Raccoon, Vidar are well-known variants) silently copy these cookies from your browser and transmit them to the attacker. With your session cookie, the attacker can authenticate to Instagram as you — without knowing your password, without triggering 2FA, without any login attempt that Instagram would flag.
Complete Protection Summary — One Fix for Every Attack Method
Here is how to make sure yours is not next.
Our complete step-by-step Instagram security guide walks through every protection above with exact settings screenshots, from enabling 2FA to recovering a compromised account.
Frequently Asked Questions – How Instagram Accounts get Hacked
Understanding attack methods is not just for hackers — it is the most effective way for everyday users to understand exactly what protection they need and why it matters. Every security recommendation in this article exists because I have seen the attack it defends against work in the real world. None of these attacks are sophisticated. All of them are preventable with the steps described above.
