Prompt Injection
+5 XP
Category
Prompt Injection
53 articles

AI LLM Hacking Course
+5 XP
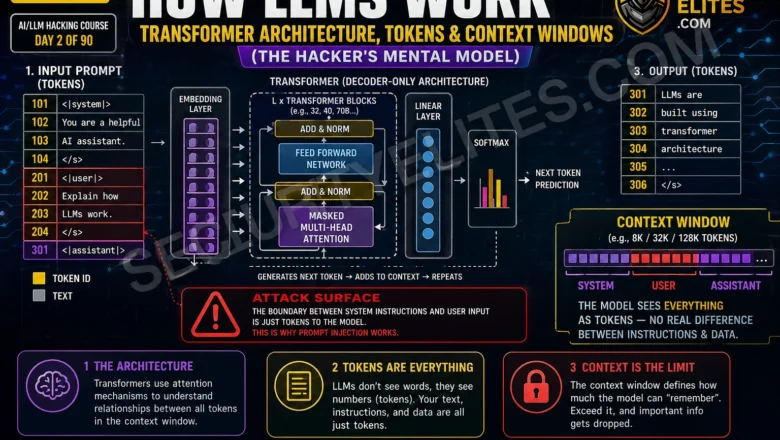
How LLMs Work — Transformer Architecture, Tokens & Context Windows | AI LLM Hacking Course Day2
Understand how LLMs work from a hacker's perspective. Tokens, attention, context windows, system vs user messages — the architecture that…
AI LLM Hacking Course
+5 XP

The AI Security Landscape 2026 — Why Every Ethical Hacker Needs to Learn LLM Hacking Now | AI LLM Hacking Course Day 1
The AI security landscape in 2026 is the biggest opportunity in ethical hacking. Learn the attack surface, OWASP LLM Top…
LLM Hacking
+5 XP

Model Poisoning Attacks 2026 — How AI Models Get Hacked From Inside
Model poisoning attacks 2026 silently manipulate AI systems. Learn how attackers corrupt training data and control AI decisions without detection.
Prompt Injection
+5 XP

Gemini Advanced Prompt Injection Vulnerabilities 2026 — Research Findings
Gemini Advanced prompt injection vulnerabilities 2026 — published research on indirect injection, tool misuse, and multi-modal attack surfaces in Google's…
Prompt Injection
+5 XP

AI Chatbot Data Exfiltration 2026 — How Prompt Injection Leaks User Data
AI chatbot data exfiltration 2026 — how prompt injection enables attackers to leak sensitive user data through covert channels. Documented…
AI in Hacking
+5 XP

AI-Powered Social Engineering 2026 — How Generative AI Makes Phishing More Dangerous
AI-powered social engineering 2026 — how LLMs are making phishing emails, vishing scripts, and spear phishing more convincing, scalable, and…
AI in Hacking
+5 XP

Autonomous AI Agents Attack Surface 2026 — Security Risks of Agentic AI
Autonomous AI agents attack surface 2026 — security risks of agentic AI with tool access, long-running tasks, and multi-agent orchestration.…
AI in Hacking
+5 XP

AI Content Filter Bypass 2026 — How Researchers Test Safety Filtering Systems
AI content filter bypass 2026 — how security researchers probe LLM safety filtering systems for weaknesses, what the findings mean…
AI in Hacking
+5 XP
Training Data Poisoning 2026 — How Attackers Corrupt AI Models Before Deployment
Training data poisoning 2026 — how attackers corrupt AI training datasets to embed backdoors, bias outputs, and degrade model performance.…