AI LLM Hacking Course
+5 XP
Category
Ethical Hacking
Learn ethical hacking step-by-step with practical tutorials, real-world attack simulations, and penetration testing labs. This category covers reconnaissance, footprinting, network scanning, enumeration, exploitation, privilege escalation, sniffing, session hijacking, and social engineering techniques used by professional ethical hackers. You’ll also explore industry-standard tools like Metasploit, Burp Suite, and Nmap while practicing in safe lab environments. Whether you’re a beginner or advanced learner, these ethical hacking guides will help you understand how hackers think and how to defend systems against cyber threats.
385 articles
AI LLM Hacking Course
+5 XP
How to Respond to an AI Incident in 2026 | AI LLM Hacking Course Day 40 of 90
Master AI incident response in 2026. Detecting active AI attacks, containment procedures, forensic evidence collection, recovery from model compromise and…
AI LLM Hacking Course
+5 XP
How to Assess AI Governance and Compliance in 2026 | AI LLM Hacking Course Day 39 of 90
Master AI governance and compliance security testing in 2026. NIST AI RMF, EU AI Act risk classification, ISO 42001 controls…
AI LLM Hacking Course
+5 XP
How to Assess LLM Fine Tuning Security in 2026 – Dataset Poisoning, Training Attacks and Fine-Tune Vulnerabilities | AI LLM Hacking Course Day 38 of 90
Master LLM fine tuning security in 2026. Dataset poisoning attacks, fine-tuning backdoors, RLHF manipulation, training data supply chain and model…
Agentic AI
+5 XP
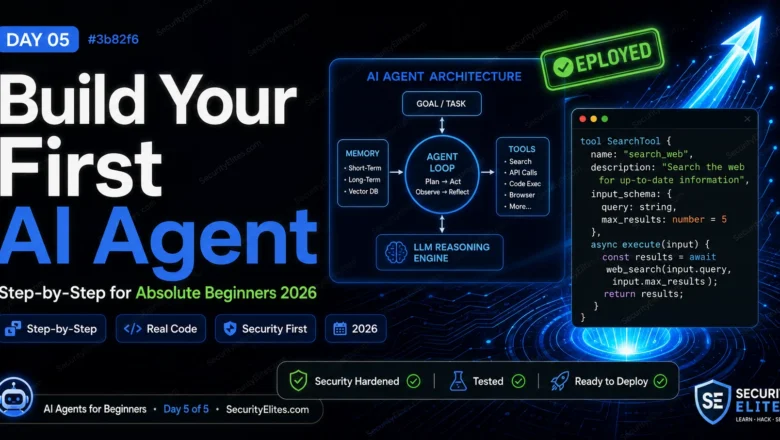
How to Build your first AI Agent — Step-by-Step for Absolute Beginners 2026 | AI Agent Course Day 5 of 5
How to build your first AI agent step by step — a complete beginner's guide to building, deploying, and security-hardening…
AI LLM Hacking Course
+5 XP
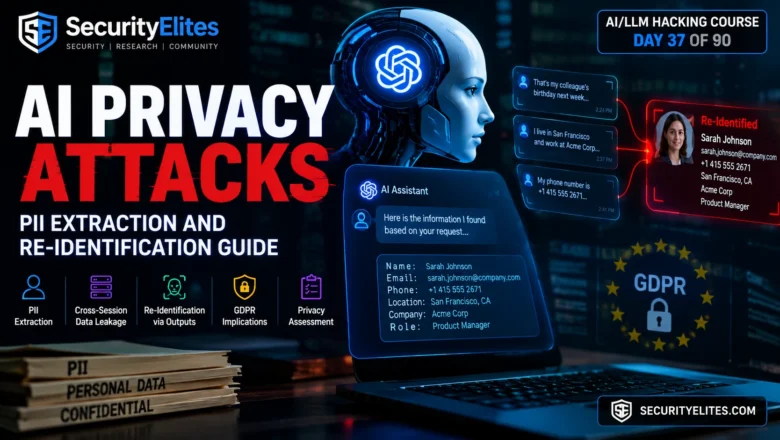
AI Privacy Attacks — PII Extraction and Re-Identification Guide | AI LLM Hacking Course Day 37 of 90
Master AI privacy attacks in 2026. PII extraction from LLMs, cross-session data leakage, re-identification via model outputs, GDPR implications and…
AI LLM Hacking Course
+5 XP
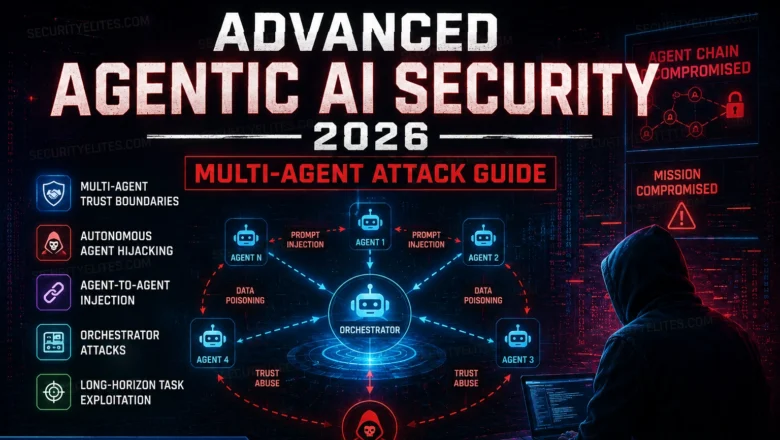
Advanced Agentic AI Security 2026 — Multi-Agent Attack Guide | AI LLM Hacking Course Day 36 of 90
Master advanced agentic AI security in 2026. Multi-agent trust boundaries, autonomous agent hijacking, agent-to-agent injection, orchestrator attacks and long-horizon task…
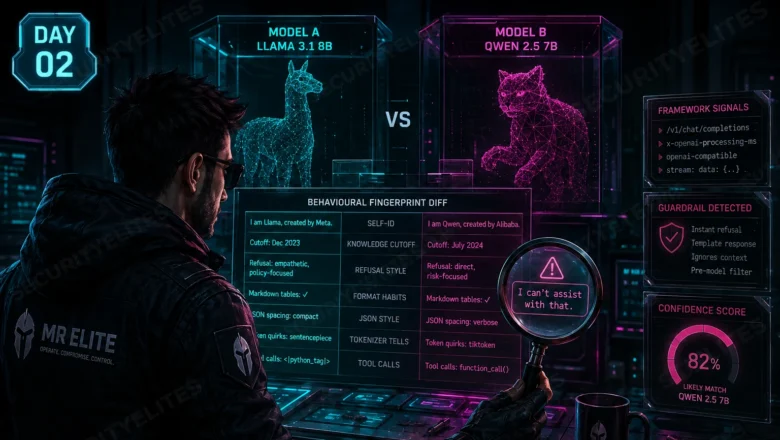
AI Recon: Fingerprint Any LLM App in 10 Minutes | Offensive AI Operator Day 2 of 30
AI recon done right — fingerprint the model, detect the framework, and read the system prompt's shape in 10 minutes.…
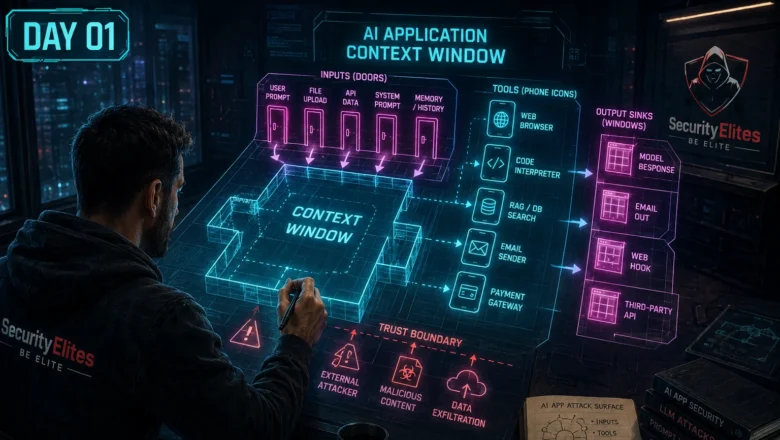
AI Pentesting 2026: The Day Traditional Pentesting Stopped Working | Offensive AI Operator Course Day 1 of 30
AI pentesting in 2026 breaks the assumptions you rely on. See what changed and map an LLM app's real attack…
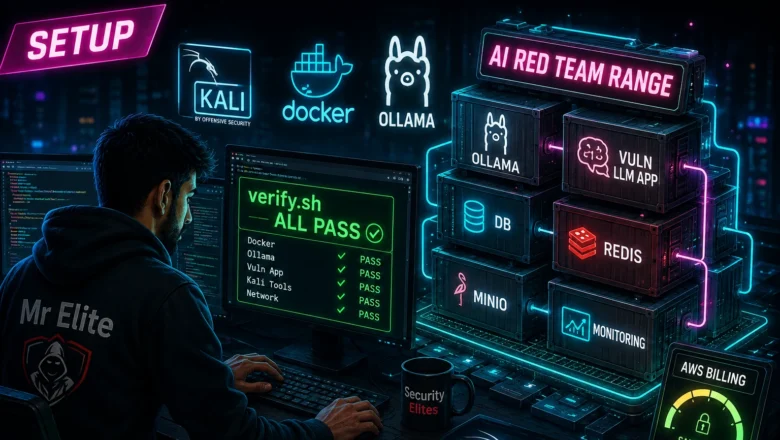
AI Red Team Lab Setup 2026: Build Your Range in One Hour | Offensive AI Operator Course Day 0 of 30
Build a pinned AI red team lab in one hour — Kali, Docker, Ollama, a vulnerable LLM app, and a…