Ethical Hacking Course
+5 XP
Category
Web Application Security
Explore web application security vulnerabilities and learn how ethical hackers identify and exploit them. This category covers SQL injection, cross-site scripting (XSS), CSRF, file upload vulnerabilities, authentication bypass, API security flaws, and session management issues. You’ll find hands-on tutorials, payload examples, exploitation labs, and prevention techniques to secure web applications. Ideal for bug bounty hunters, penetration testers, and developers who want to build and test secure web platforms.
103 articles
Bug Bounty Course
+5 XP
Day 7: XSS Bug Bounty Hunting — Find, Exploit & Report Cross-Site Scripting Bugs That Pay (2026)
Complete XSS bug bounty hunting guide — where to find reflected, stored, and DOM XSS, Burp Suite Repeater workflow, filter…
Ethical Hacking Course
+5 XP
Day 18: File Upload Vulnerabilities — From Image Upload to Web Shell (2026)
Understand file upload vulnerabilities from first principles — how validation is bypassed, how web shells work, full DVWA demos at…
Bug Bounty Hunting
+5 XP
Google Bug Bounty Program — How Ethical Hackers Legally Earn $100–$31,337 Finding Gmail Vulnerabilities (2026)
Learn how ethical hackers legally earn $100 to $31,337 through Google's Vulnerability Reward Program aka Google Bug Bounty Program. Scope,…
Ethical Hacking Course
+5 XP
Day 17: Security Misconfiguration — The Easiest Vulnerabilities to Find (2026)
Day 17 of 100. Learn security misconfiguration — default credentials, verbose errors, exposed admin panels, open cloud buckets, directory listing,…
Cyber Security
+5 XP
How to Secure Gmail Account From Hackers — The Ultimate 2026 Protection Guide (Block Every Attack)
Complete step-by-step guide on how to secure Gmail account — enabling 2-Step Verification with an authenticator app, reviewing account activity,…
Ethical Hacking Course
+5 XP
Day 16: Broken Access Control & IDOR — The #1 Web Vulnerability Explained (2026)
Day 16 of 100. Master Broken Access Control — including IDOR, horizontal & vertical privilege escalation, directory traversal, and mass…
Bug Bounty Course
+5 XP
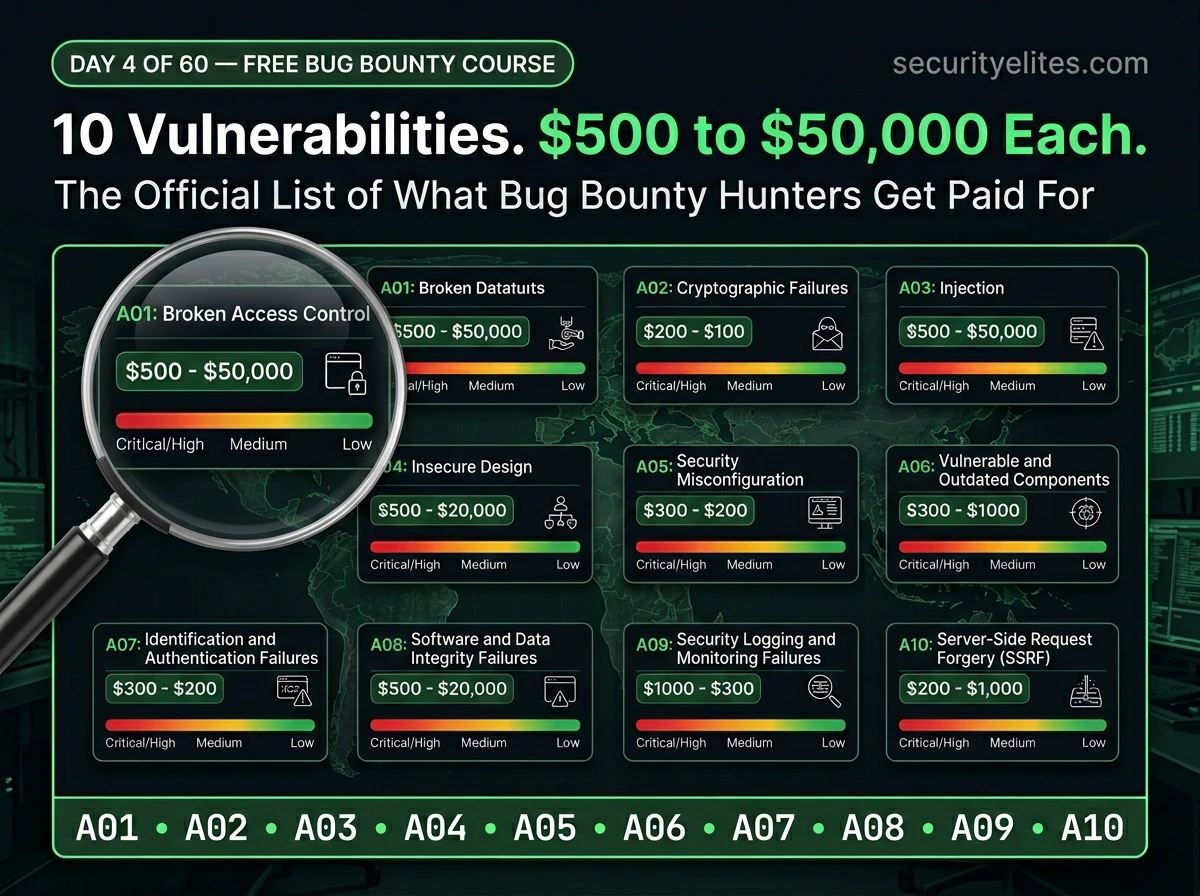
Day 4: OWASP Top 10 Explained — The Official Bug Bounty Vulnerability Map Every Hunter Needs (2026)
Day 4 of 60. Learn the OWASP Top 10 in plain English — what each vulnerability is, how it’s exploited,…
Ethical Hacking Course
+5 XP
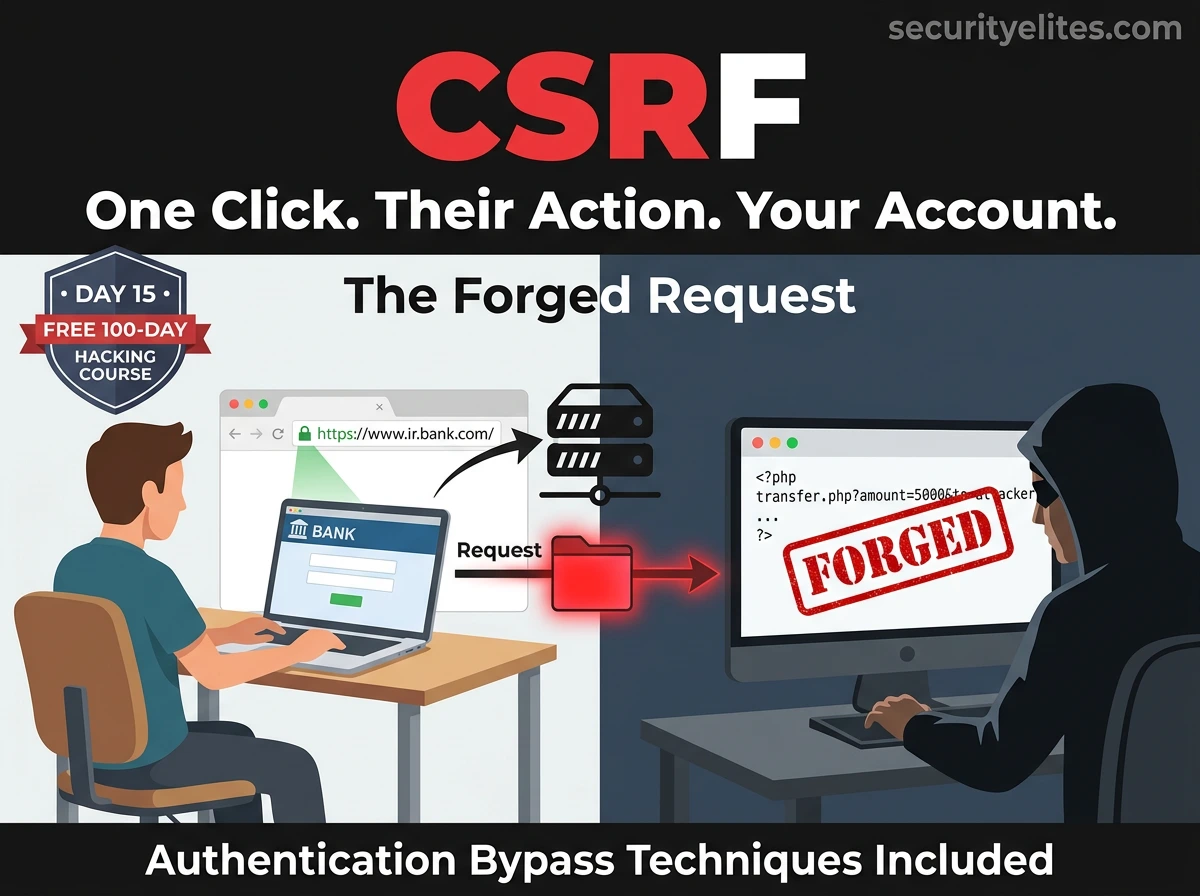
Day 15: CSRF & Authentication Bypass — When Web Requests Get Forged (2026)
Day 15 of 100. CSRF attacks explained, understand authentication bypass — how forged requests exploit user trust, CSRF tokens, SameSite…
Ethical Hacking Course
+5 XP
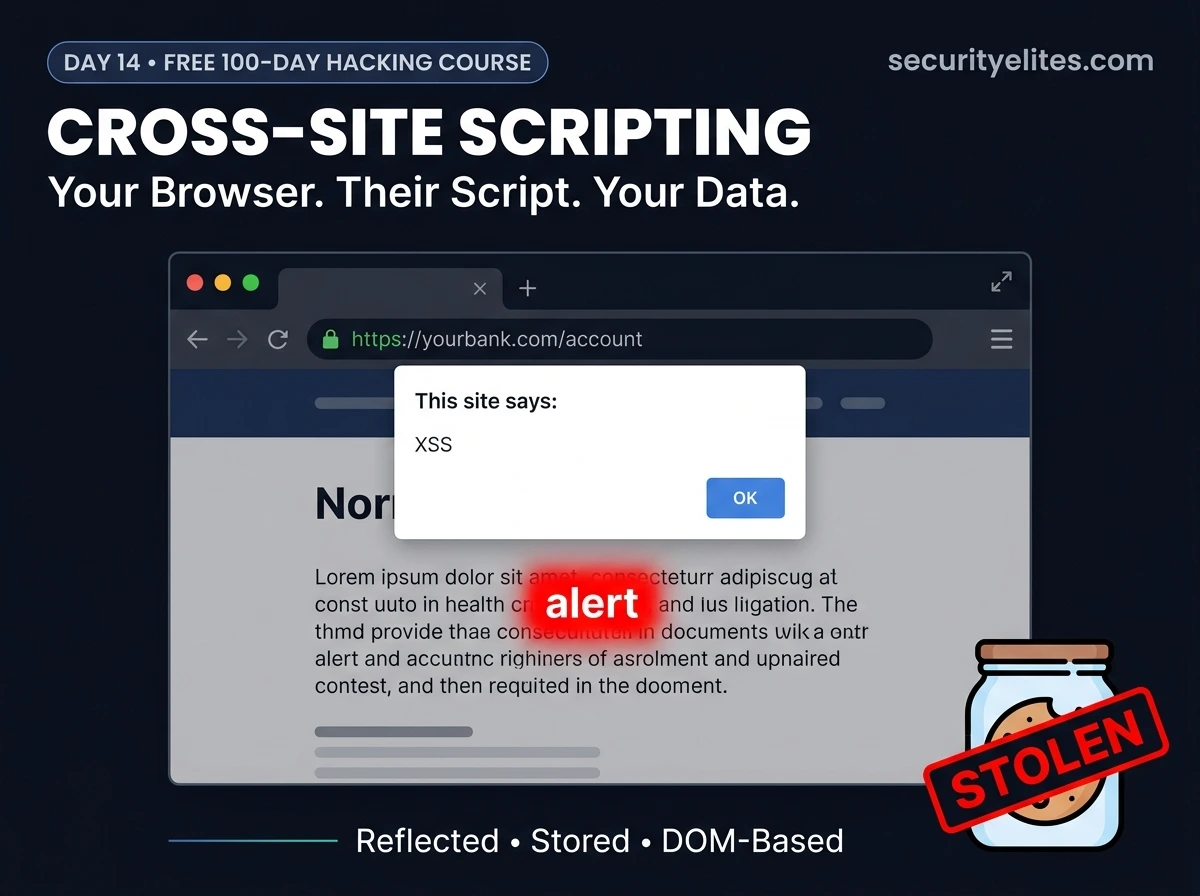
Day 14: XSS Cross-Site Scripting — How Hackers Steal Cookies & Take Over Accounts (2026)
Day 14 of 100. Understand XSS Cross Site Scripting —reflected, stored, and DOM-based—with DVWA demos in Burp Suite, cookie theft…