DVWA Labs
+5 XP
Category
Web Application Security
Explore web application security vulnerabilities and learn how ethical hackers identify and exploit them. This category covers SQL injection, cross-site scripting (XSS), CSRF, file upload vulnerabilities, authentication bypass, API security flaws, and session management issues. You’ll find hands-on tutorials, payload examples, exploitation labs, and prevention techniques to secure web applications. Ideal for bug bounty hunters, penetration testers, and developers who want to build and test secure web platforms.
103 articles
DVWA Labs
+5 XP
Lab 5: DVWA File Inclusion Lab 2026 — Hack Hidden Files in 1 Minute
Complete DVWA File Inclusion lab 2026 — exploit LFI to read /etc/passwd, path traversal, PHP wrappers, and RFI remote code…
Ethical Hacking Course
+5 XP
Day 25: Kerberoasting 2026 — Attack & Defend Service Account Passwords in Active Directory
Master Kerberoasting in 2026 — request Kerberos service tickets, extract TGS hashes, crack offline with Hashcat, and detect attacks as…
Bug Bounty Course
+5 XP
XXE Injection Bug Bounty 2026 — Day 13 Hack Server Files via XML
Master XXE injection bug bounty 2026 — find XML external entity vulnerabilities, read server files, SSRF via XXE, blind XXE…
DVWA Labs
+5 XP
Lab 4: DVWA CSRF Lab 2026 — Forge Cross-Site Requests & Bypass Token Validation
Complete DVWA CSRF lab 2026 — forge cross-site requests, change passwords, bypass token validation at all 4 security levels. Hands-on…
DVWA Labs
+5 XP
Lab 3: DVWA Command Injection Lab 2026 — Inject OS Commands & Get a Reverse Shell
Master DVWA command injection lab 2026 — inject OS commands at all 4 security levels, bypass filters & establish a…
Bug Bounty Course
+5 XP
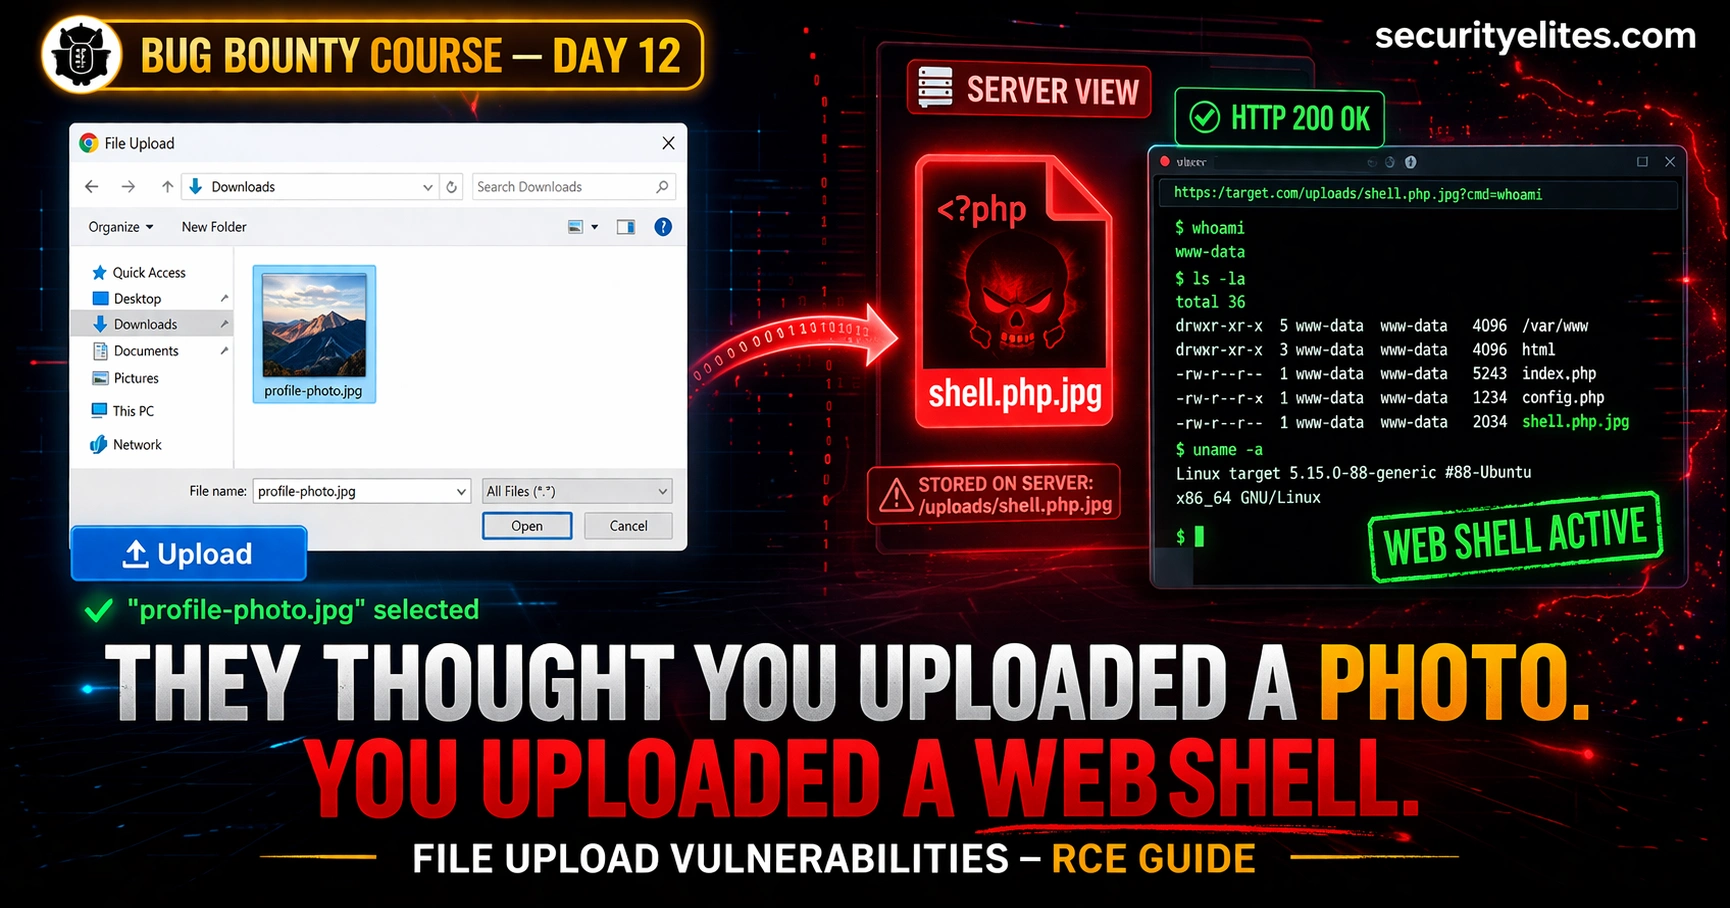
Day 12: File Upload Vulnerabilities — From Bypassing Filters to Remote Code Execution (Bug Bounty 2026)
File upload vulnerabilities bug bounty are among the highest-paying bugs in bounty programs. Day 12 covers every bypass technique—from MIME…
Session Hijacking
+5 XP
Browser-Based Attacks 2026 — AITM Phishing, ClickFix and Session Hijacking Are Driving the Biggest Breaches Right Now (Complete Guide)
AITM phishing, ClickFix malware and session hijacking are behind today's biggest corporate breaches. Here's exactly how browser-based attacks works and…
Cyber Security News
+5 XP
Cisco CVE-2026-20093 — CVSS 9.8 Authentication Bypass Explained: How Hackers Get Admin Access Without a Password (2026)
Cisco patched Cisco CVE-2026-20093 authentication bypass, a CVSS 9.8 critical flaw letting unauthenticated attackers bypass authentication and gain admin access.…
Bug Bounty Course
+5 XP
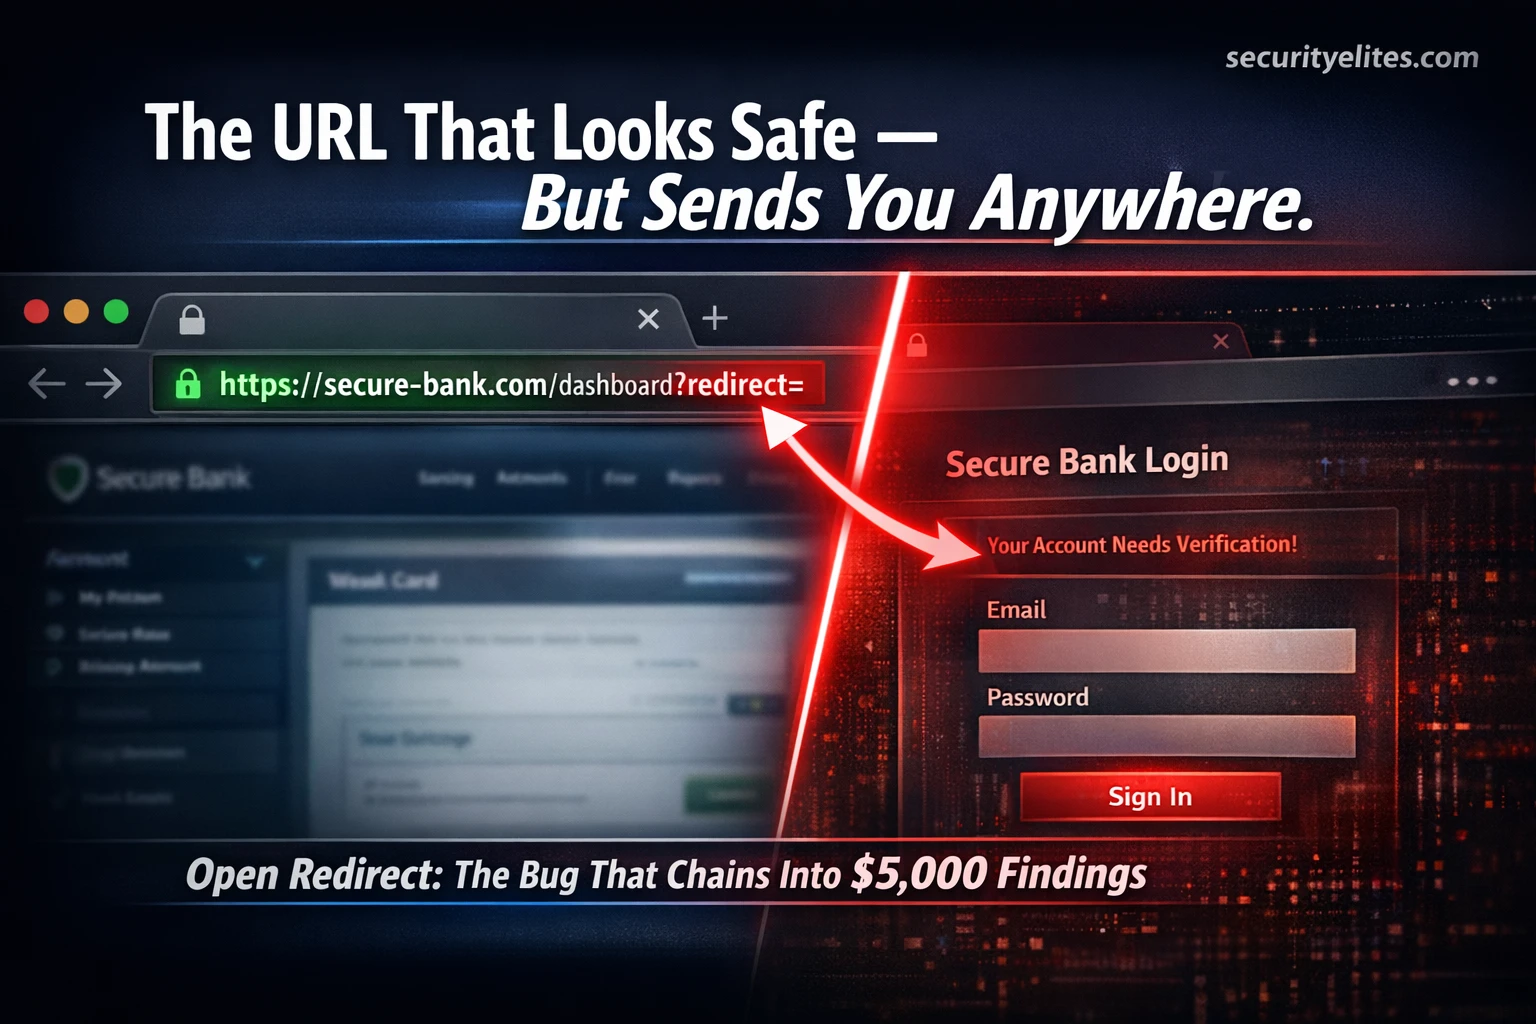
Day 11: Open Redirect Bug Bounty Hunting 2026 — Find, Chain and Report the Vulnerability That Turns $200 Bugs Into $5,000 Findings
Day 11 of 60. Master open redirect bug bounty hunting with manual testing, bypass techniques, OAuth chaining for account takeover,…