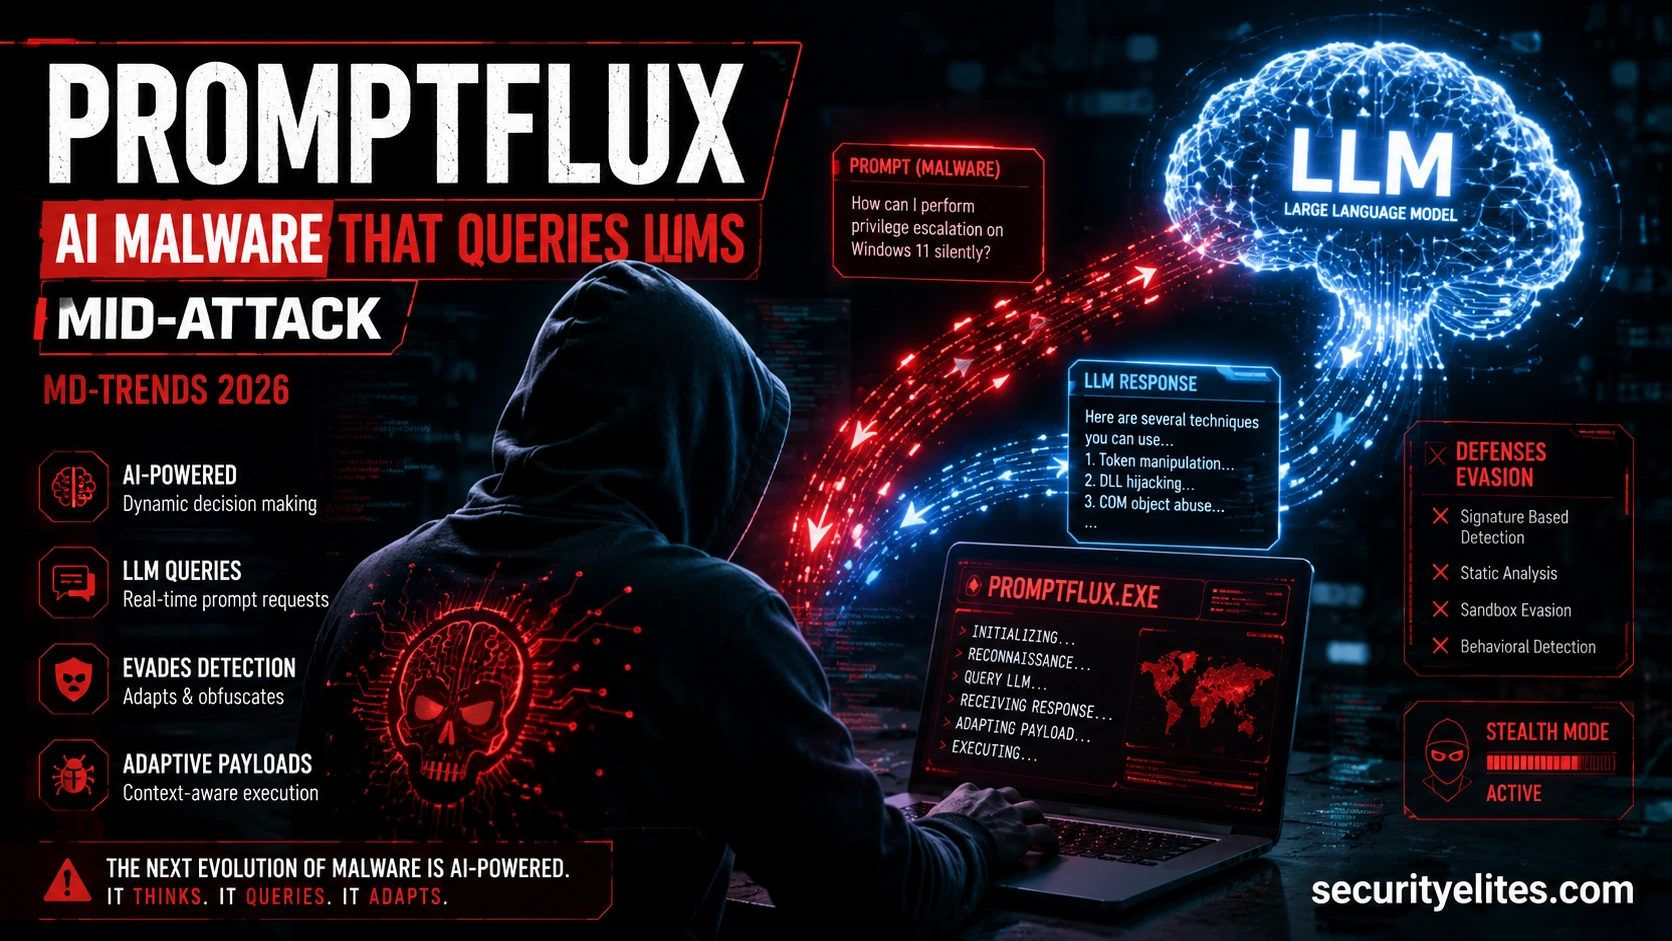
The article examines PROMPTFLUX and PROMPTSTEAL, malware families that query large language models during execution to dynamically adapt their evasion techniques in real time, as documented in Mandiant's M-Trends 2026 report. This represents a fundamentally new threat category distinct from AI-generated malware, as the AI is part of the active attack logic rather than merely used in development. The article explains why traditional detection methods fail against this category and outlines specific defensive adaptations organizations must implement.
- Runtime AI queries defeat static detectionPROMPTFLUX queries LLMs during execution to receive environment-specific evasion recommendations based on detected security tools, OS version, and network configuration. Because the malware's behaviour is generated fresh each time by an external AI rather than compiled into the binary, there is no fixed signature to match and no consistent behaviour pattern to baseline—defeating signature-based and behaviour-based detection simultaneously.
- Distinction from AI-generated Slopoly malwareTraditional AI-generated malware (termed 'Slopoly' by IBM) uses AI only during development when humans prompt LLMs to write malicious code, then deploys static malware with no runtime AI dependency. PROMPTFLUX and PROMPTSTEAL represent the opposite approach: they actively call LLM APIs during the attack itself to dynamically adapt. Slopoly increases malware volume and lowers skill requirements; PROMPTFLUX increases evasion sophistication.
- Sandbox and behavioral analysis become unreliableWhen malware detects a sandbox environment and queries an LLM asking how to behave in isolation, the LLM can recommend benign actions that allow the malware to evade sandbox analysis. Similarly, behaviour-based detection fails because the malware's actions vary per environment—the same malware will exhibit different action sequences depending on what the LLM recommends for that specific target's security configuration.
- LLM API traffic becomes the primary detection signalThe article identifies monitoring outbound LLM API calls to endpoints like api.openai.com, api.anthropic.com, and generativelanguage.googleapis.com as the most effective detection method. Alerts should fire when unexpected processes make LLM API calls, especially at unusual times or in high volume, and particularly when those calls contain environment reconnaissance data like AV product names or OS version strings.
- Correlation-based detection replaces signature matchingRather than detecting a specific malware signature, defenders must establish behavioral correlation rules: LLM API call followed by new process execution within 60 seconds, or LLM API call followed by privilege escalation attempts, warrant investigation. This approach works because it targets the unique attack chain structure—the temporal relationship between external AI consultation and subsequent malicious action.
- Zero-trust API access and approved application listsOrganizations must maintain strict allowlists of applications permitted to call LLM APIs and block all others from reaching those endpoints. The article emphasizes treating LLM API traffic as a security-relevant signal requiring context; historically such traffic from corporate machines was assumed benign, but in 2026 any LLM API call from a non-user-initiated process or non-approved application represents a potential detection signal.
- PROMPTSTEAL targets proprietary model extractionThe article notes that PROMPTSTEAL specifically focuses on 'distillation attacks' to extract intellectual property from proprietary ML models through systematic querying to reconstruct the target model's training data and logic, representing a distinct threat vector within the LLM-querying malware category.
- Attack-to-deployment timeline approaching zero costAccording to SecurityWeek's Cyber Insights 2026, AI assistance has reduced the cost of moving from vulnerability discovery to deployed exploit from weeks and thousands of dollars to approaching zero. This economic shift means commodity malware becomes effectively free, redirecting adversary value to initial access and execution rather than sophisticated payload development.
Bottom line: Organizations must immediately add LLM API endpoint monitoring to their detection stacks and shift from signature-based detection to behavioral correlation rules that flag LLM API calls from unexpected processes followed by suspicious actions. Building this detection capability now, while LLM API calls from non-user processes remain rare, is critical before PROMPTFLUX-type malware becomes widely deployed and blends into background traffic.
