Authentication Bypass
+5 XP
Category
Web Application Security
Explore web application security vulnerabilities and learn how ethical hackers identify and exploit them. This category covers SQL injection, cross-site scripting (XSS), CSRF, file upload vulnerabilities, authentication bypass, API security flaws, and session management issues. You’ll find hands-on tutorials, payload examples, exploitation labs, and prevention techniques to secure web applications. Ideal for bug bounty hunters, penetration testers, and developers who want to build and test secure web platforms.
103 articles
DVWA Labs
+5 XP
Lab11 : DVWA SQL Injection Blind Lab 2026 — Boolean and Time-Based Blind SQLi Guide
DVWA sql injection blind lab 2026 — extract database data using boolean-based and time-based blind techniques when no output is…
DVWA Labs
+5 XP
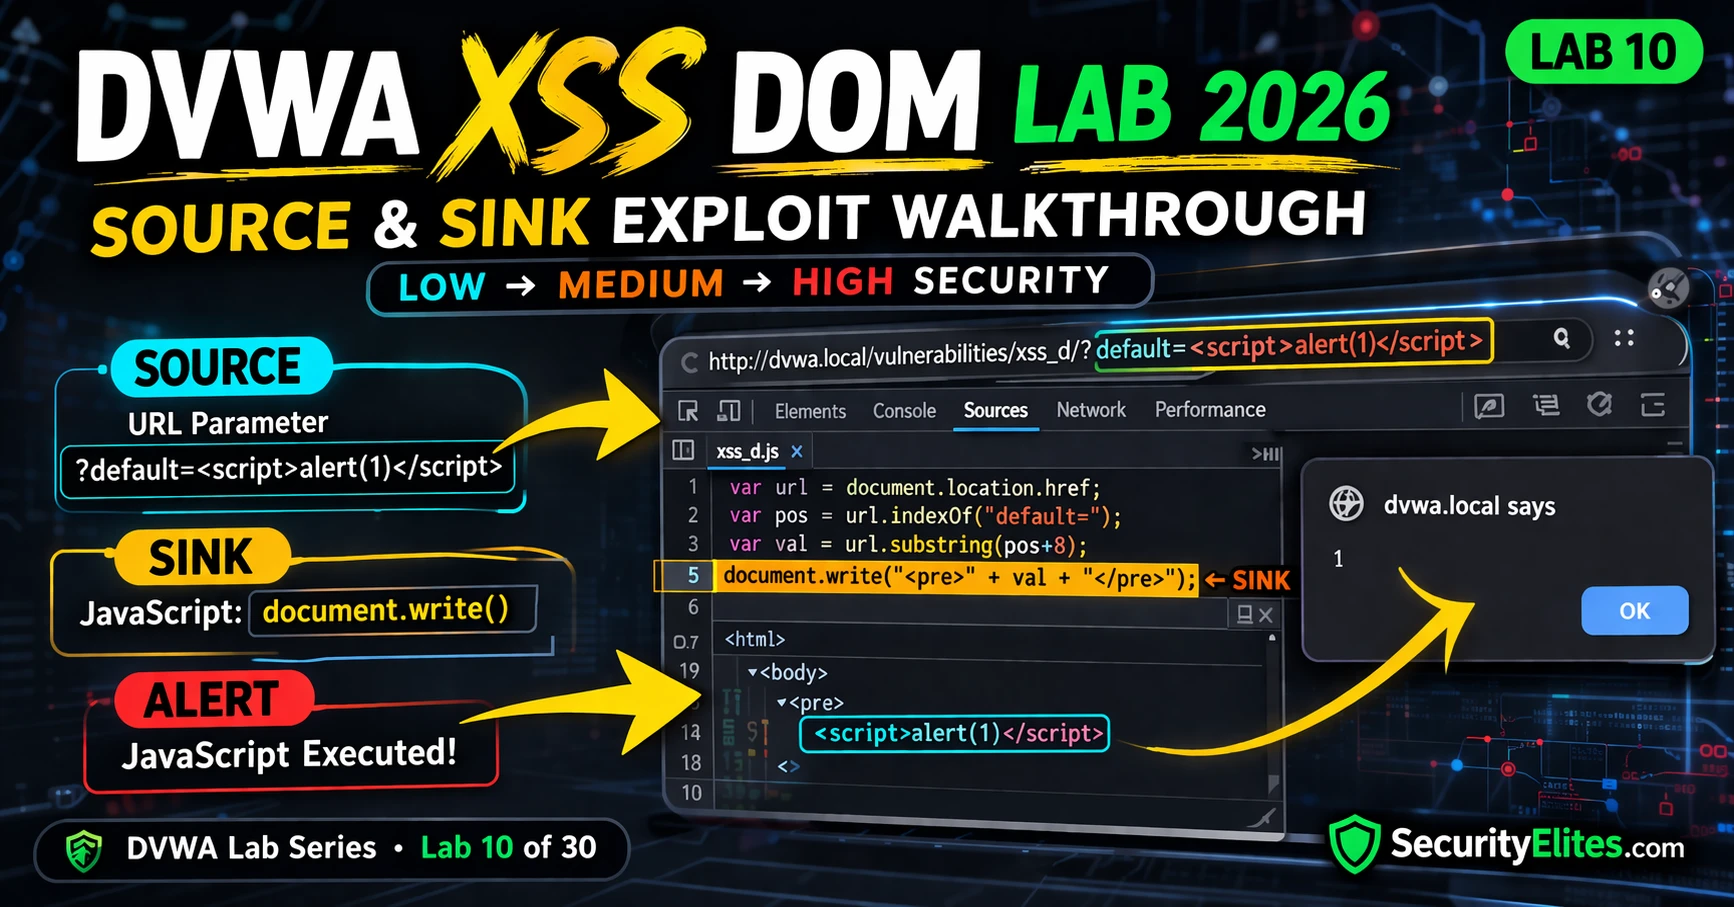
Lab 10: DVWA XSS DOM Lab 2026 — The Hidden Vulnerability You Can Exploit Instantly
DVWA XSS DOM lab 2026 — complete walkthrough for DOM-based cross-site scripting at Low, Medium and High security. Source and…
DVWA Labs
+5 XP
Lab 9: DVWA XSS Stored Lab 2026 — One Payload Hacks Every User (Persistent XSS Exploit Guide)
DVWA xss stored lab 2026 — inject persistent JavaScript payloads into the guestbook, escalate to cookie theft affecting all users,…
Bug Bounty Course
+5 XP
BB Day15: Business Logic Vulnerabilities Bug Bounty 2026 — Bypass Payment Like a Hacker
Business logic vulnerabilities bug bounty 2026 — find price manipulation, workflow bypass and privilege escalation flaws that scanners miss. Day…
DVWA Labs
+5 XP
Lab 8: DVWA XSS Reflected Lab 2026 — Steal Cookies in Seconds & Bypass Filters Like a Hacker
DVWA xss reflected lab 2026 — inject JavaScript payloads at all 4 security levels, steal session cookies with Burp, bypass…
DVWA Labs
+5 XP
Lab 7: DVWA SQL Injection Lab 2026 — Manual Injection to Full Database Dump Complete Guide
DVWA sql injection lab 2026 — manual injection at all 4 security levels, extract usernames and passwords, bypass filters and…
Cloud Hacking
+5 XP
How to Hack AWS S3 Buckets (Ethically) 2026 — 5 Real Misconfigurations Exposed
Hack aws s3 buckets ethically 2026 — discover 5 real S3 misconfigurations, enumerate public buckets, test ACL weaknesses and report…
Ethical Hacking Course
+5 XP
Day 26: Pass the Hash & Pass the Ticket 2026 — Lateral Movement With NTLM & Kerberos
Pass the hash & pass the ticket 2026 — exploit NTLM hashes and Kerberos tickets for lateral movement in Active…
Bug Bounty Course
+5 XP
BB Day 14: Command Injection Bug Bounty 2026 — Find OS Injection in Web Apps & APIs That Pay
Command injection bug bounty 2026 — find OS command injection in web apps and APIs, bypass filters, chain with SSRF…