DVWA Labs
+5 XP
Category
Web Application Security
Explore web application security vulnerabilities and learn how ethical hackers identify and exploit them. This category covers SQL injection, cross-site scripting (XSS), CSRF, file upload vulnerabilities, authentication bypass, API security flaws, and session management issues. You’ll find hands-on tutorials, payload examples, exploitation labs, and prevention techniques to secure web applications. Ideal for bug bounty hunters, penetration testers, and developers who want to build and test secure web platforms.
103 articles
DVWA Labs
+5 XP
DVWA Brute Force Advanced Lab 2026 — Anti-CSRF Token Bypass Complete Walkthrough | Hacking Lab15
DVWA brute force advanced lab 2026 — bypass anti-CSRF token protection at High security using Burp Suite macros to extract…
DVWA Labs
+5 XP
Lab14: DVWA Security Levels Explained 2026 — Low, Medium, High & Impossible Complete Guide
DVWA security levels explained 2026 — understand what Low, Medium, High and Impossible settings change in every module's source code.…
Bug Bounty Course
+5 XP
BB Day18: OAuth 2.0 Bug Bounty 2026 — CSRF in OAuth, Token Leakage & Account Takeover Chains
OAuth bug bounty 2026 — find CSRF in OAuth flows, token leakage via referrer, account takeover chains and open redirect…
DVWA Labs
+5 XP
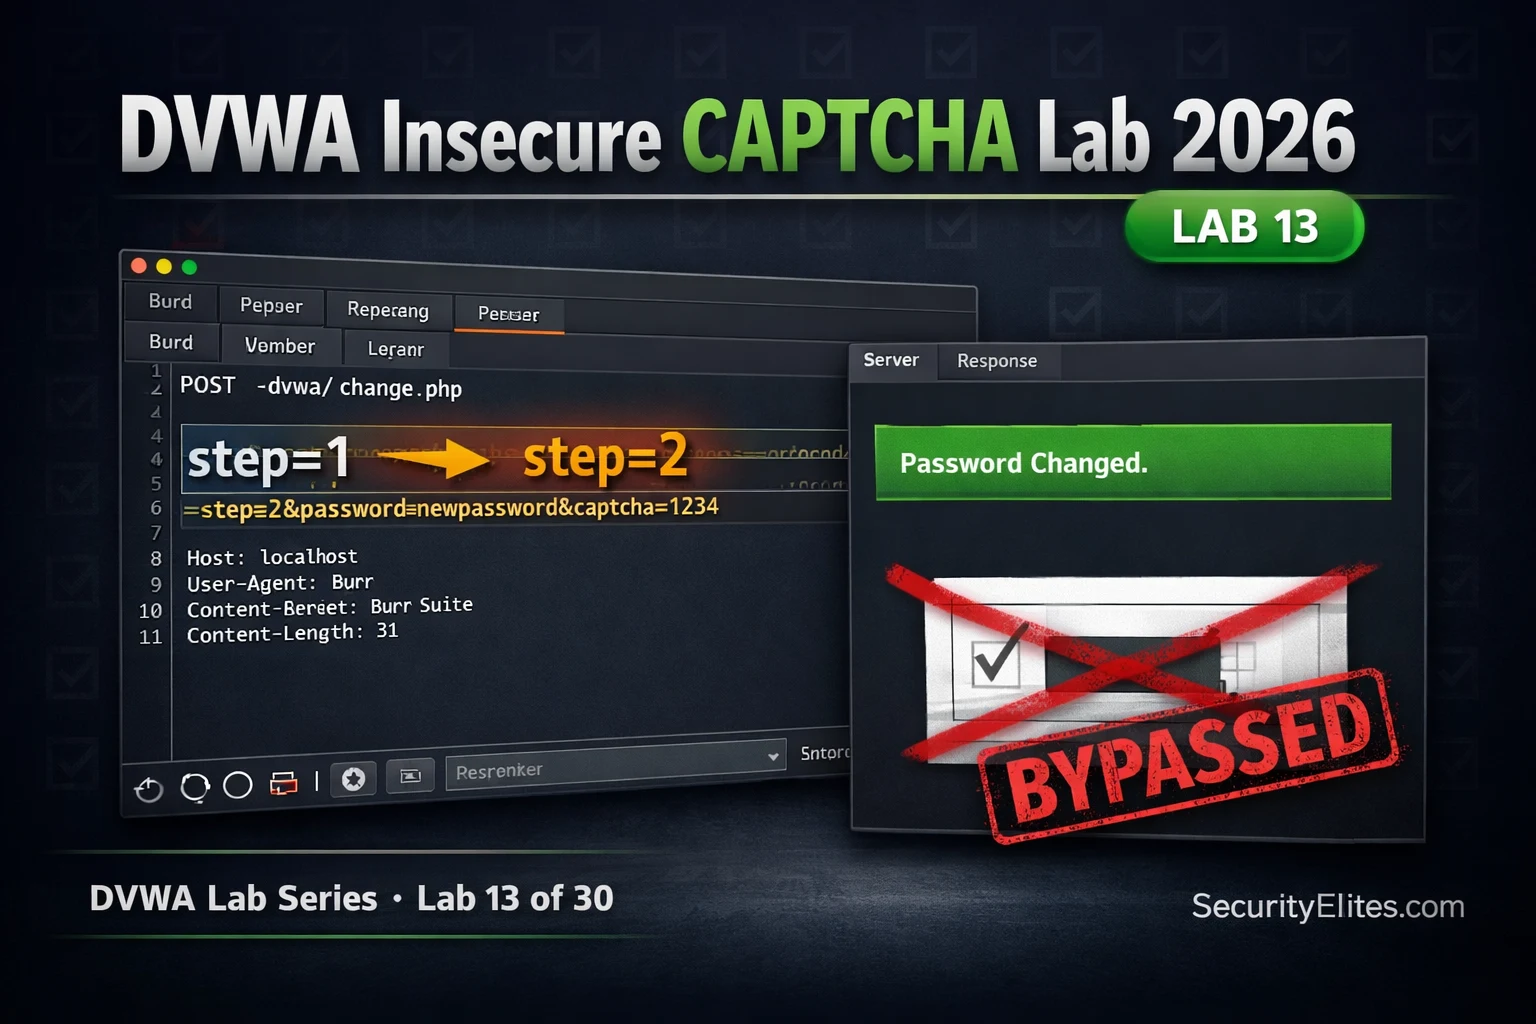
Lab13: DVWA Insecure CAPTCHA Lab 2026 — Bypass Logic & Complete Walkthrough
DVWA insecure captcha lab 2026 — bypass CAPTCHA logic flaws at all security levels using Burp Suite. Complete walkthrough with…
Ethical Hacking Course
+5 XP
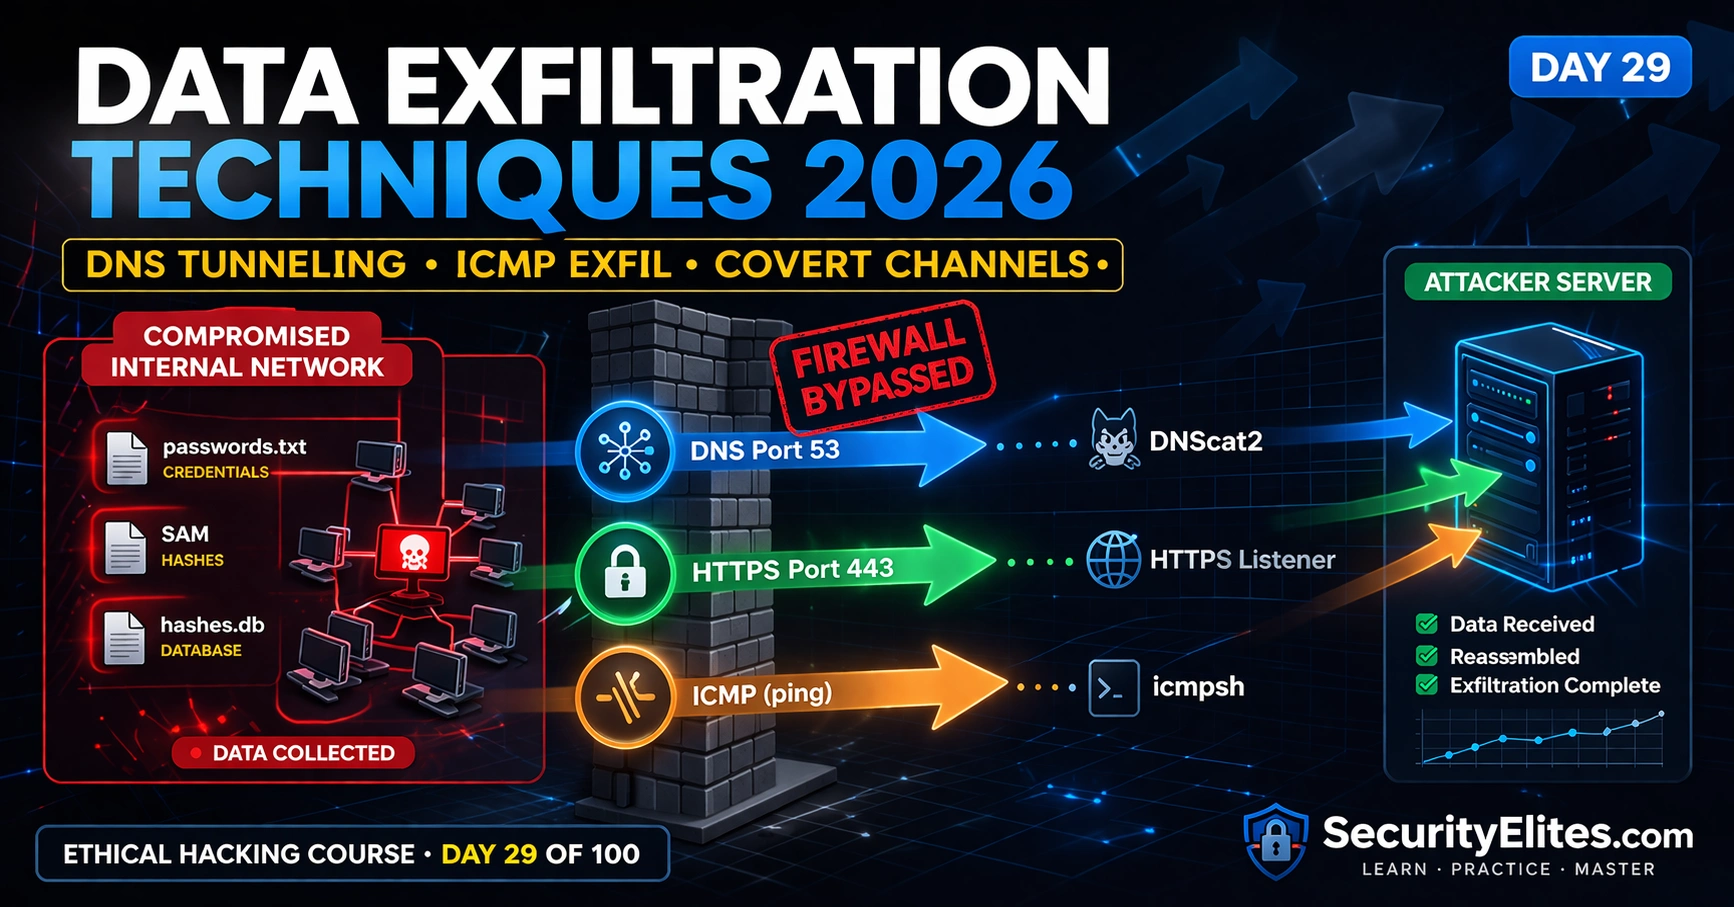
Data Exfiltration Techniques 2026 — DNS Tunneling, ICMP Exfil & Covert Channels | Hacking Course Day29
Data exfiltration techniques 2026 — move collected data out of compromised networks using DNS tunneling, ICMP covert channels and HTTPS…
Bug Bounty Course
+5 XP
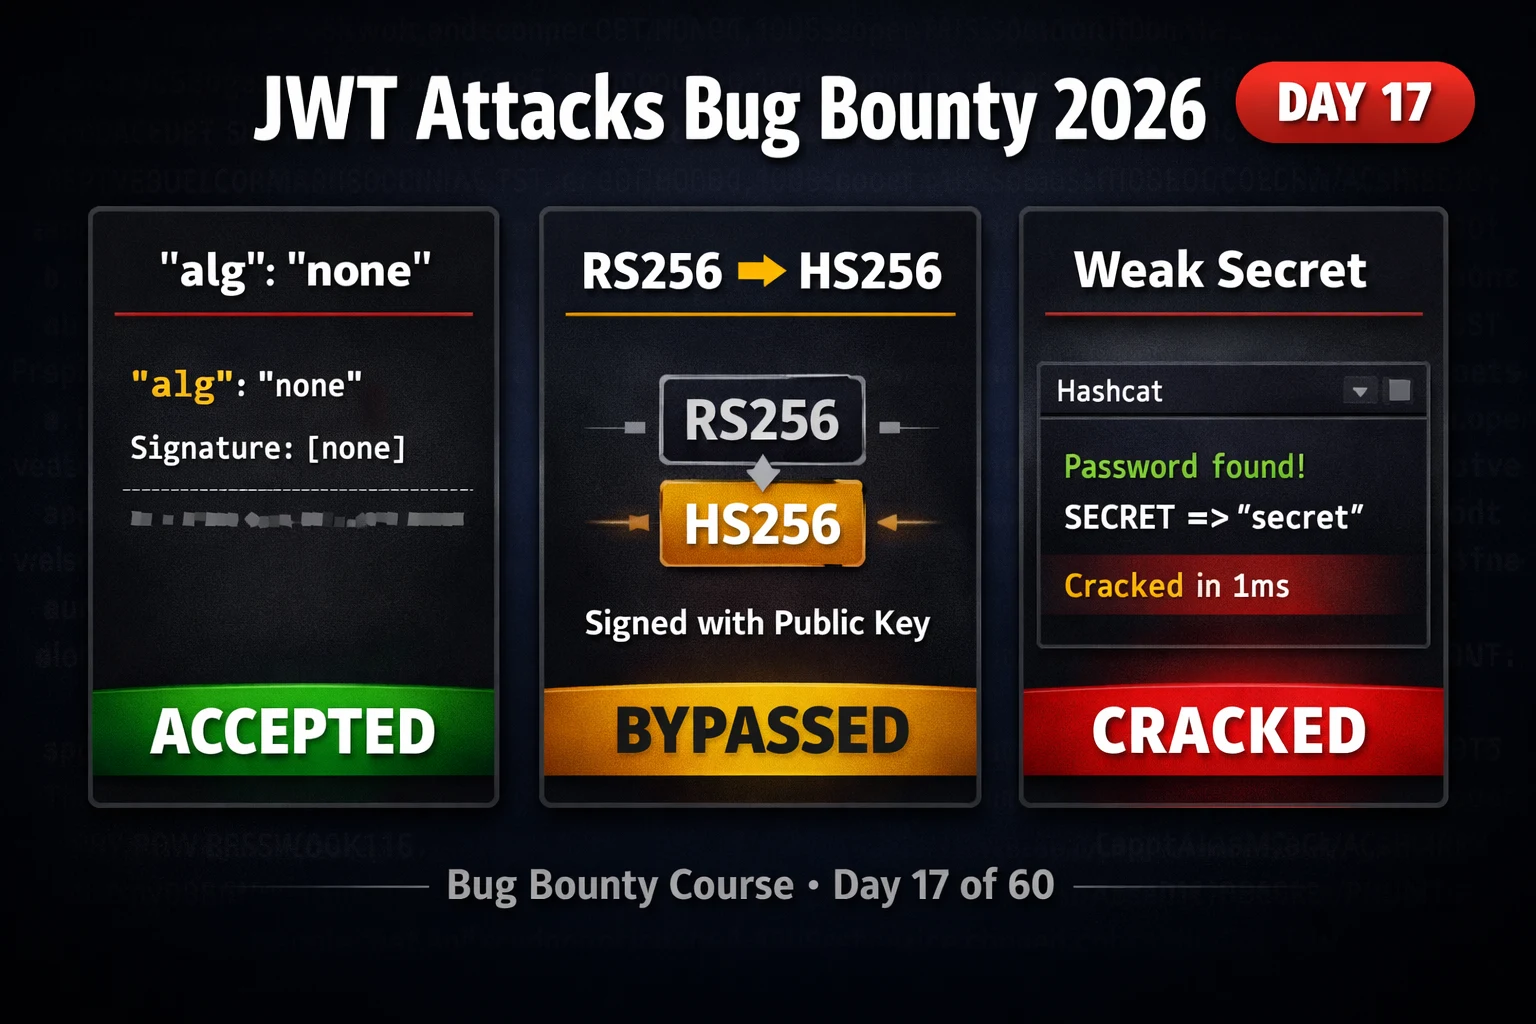
BB Day17: JWT Attacks Bug Bounty 2026 — Algorithm Confusion, None Attack & Weak Secrets
JWT attacks bug bounty 2026 — exploit algorithm confusion, none attack, weak signing secrets and kid injection in JSON web…
AI in Hacking
+5 XP
ChatGPT Plugins Are a Security Nightmare — Here’s How Hackers Exploit Them
ChatGPT plugin security vulnerabilities 2026 — how attackers exploit insecure plugins to exfiltrate data, bypass restrictions, and hijack AI tool…
DVWA Labs
+5 XP
Lab12 : DVWA SQLmap Lab 2026 — The Exact SQLmap Workflow Hackers Use in 2026
DVWA SQLmap lab 2026 — automate complete database extraction using SQLmap against DVWA SQL injection. Tables, columns, data dump and…
Ethical Hacking Course
+5 XP
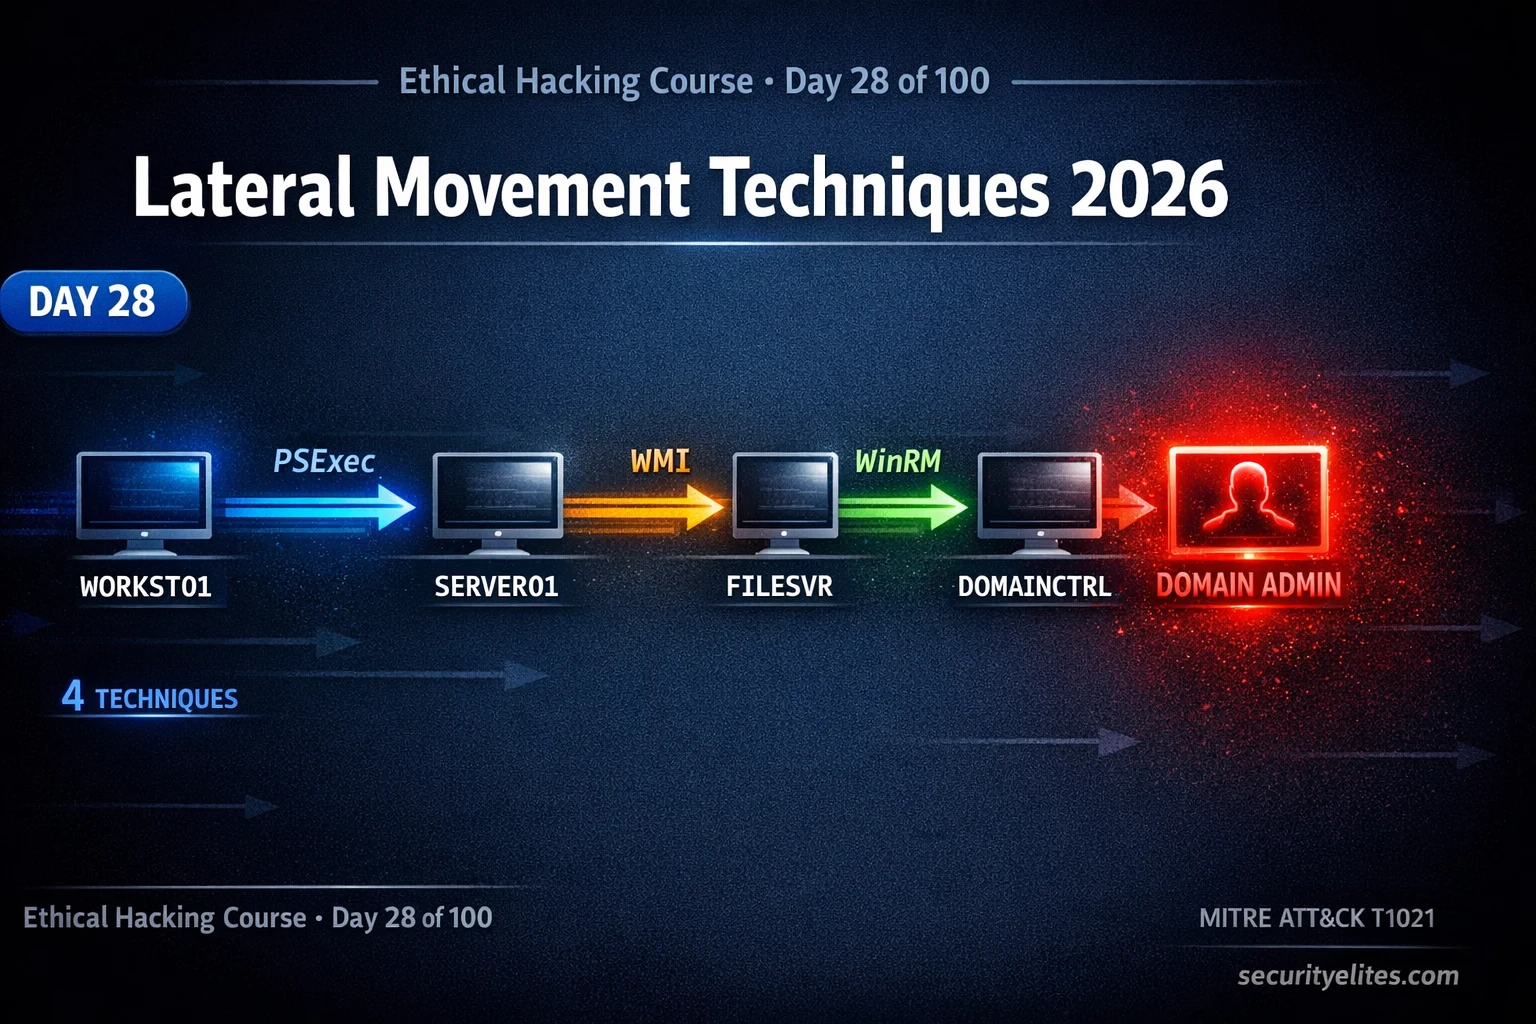
Lateral Movement Techniques 2026 — Execute Every BloodHound Attack Path in AD | Hacking Course Day 28
Lateral movement techniques 2026 — execute BloodHound attack paths using PSExec, WMI, WinRM and DCOM to move through Active Directory…