AI LLM Hacking Course
+5 XP
Category
Red Team
138 articles
AI LLM Hacking Course
+5 XP
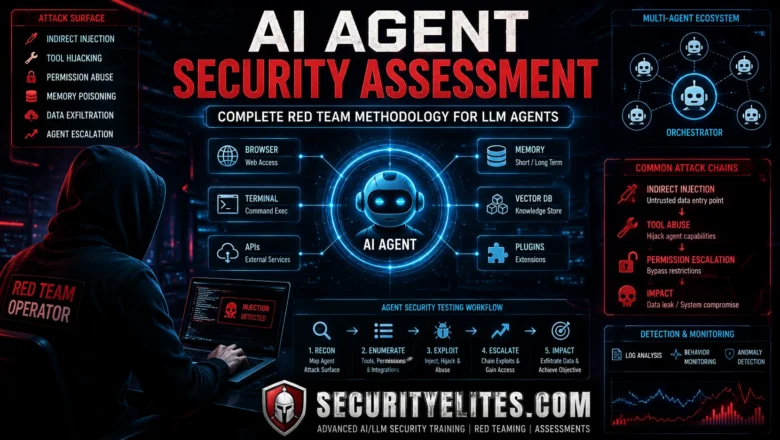
How to Conduct an AI Agent Security Assessment in 2026 | Day 19
Complete AI agent security assessment methodology in 2026. Permission mapping, tool hijacking, indirect injection chains, multi-agent security and professional report…
Kali Linux Course
+5 XP
Msfvenom Tutorial – How to Use Msfvenom to Generate Payloads | Kali Linux Day 27
Msfvenom tutorial in Kali Linux. Staged vs stageless payloads, Windows/Linux/Android backdoors, encoding with shikata_ga_nai, and multi/handler setup.
AI in Hacking
+5 XP
Post-Quantum Cryptography — What Security Teams Must Do Before It’s Too Late
Post-quantum cryptography. Why harvest-now-decrypt-later attacks are already happening, what NIST PQC standards mean for your organisation, and the migration timeline.
AI LLM Hacking Course
+5 XP
How to Extract a System Prompt Using Advanced Techniques in 2026 | Day 18
Master How to extract a system system prompt using Advanced Techniques in 2026. 15 ranked techniques, model resistance profiling, Burp…
AI LLM Hacking Course
+5 XP
How to Use Burp Suite for LLM Security Testing | Day17
Use Burp Suite for LLM security testing in 2026. Intercept AI API traffic, manipulate prompts in the proxy, build custom…
AI Security Posture Management – The Security Tool Every Organisation Needs
What is AI-SPM? AI Security Posture Management explained — what it monitors, how it differs from CSPM, the top tools…
AI LLM Hacking Course
+5 XP
How to Build an Automated Prompt Injection Testing Pipeline | Day 16
Build automated prompt injection testing pipelines in 2026. Payload libraries, multi-model scanning, rate-aware fuzzing and evidence collection — Day 16…
Metasploitable Labs
+5 XP
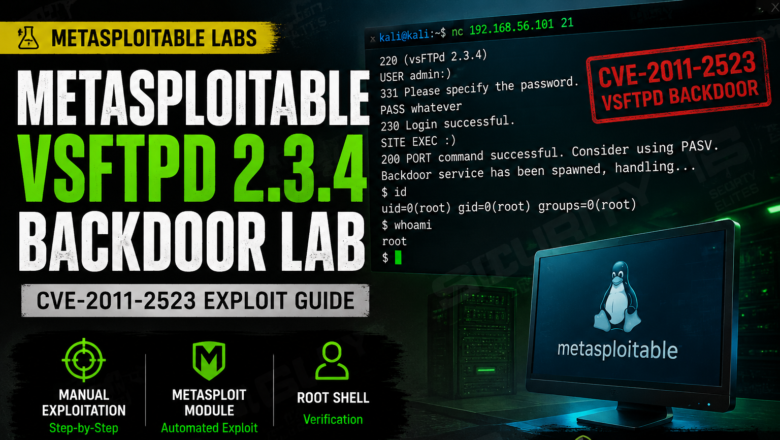
Metasploitable vsftpd Backdoor Lab — CVE-2011-2523 Exploit Guide
Exploit vsftpd 2.3.4 backdoor on Metasploitable 2026. CVE-2011-2523 manual exploitation, Metasploit module, root shell verification and remediation. Lab 5 guide.
AI in Hacking
+5 XP
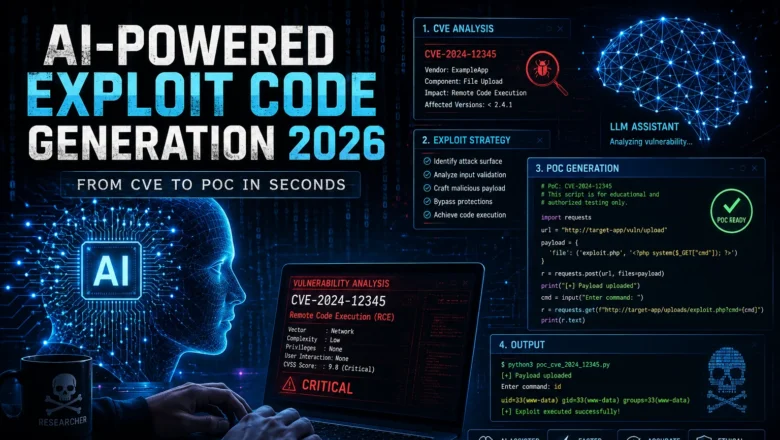
AI-Powered Exploit Code Generation — From CVE to PoC in Seconds
AI-powered exploit code generation. How LLMs assist security researchers creating proof-of-concept code, from CVE analysis to PoC drafting, limitations, and…